North Dallas office, 5757 Alpha Rd
Cybersecurity Services in Dallas, TX
Monitored around the clock, priced in public, and built to Texas breach law from day one.
MSP 501, 7 years running | SOC 2 Type 1 report, 2023 | 120-day guarantee | From $40 per user per month
Uprite provides cybersecurity services in Dallas for small and mid-sized businesses, with 24/7 threat monitoring, endpoint detection and response, email and identity protection, firewall management, vulnerability scanning, and incident response run from our North Dallas office. Security-only plans start at $40 per user per month for companies that already have IT staff. Fully managed IT with the security stack built in starts at $138 per user per month. If you want the whole picture, security sits inside our managed IT services in Dallas, and every plan carries a 120-day exit and a rate that won’t rise in year one.
What DFW breach filings show
Dallas Breaches Aren’t the Ones on the News
Ask a Dallas owner what a breach looks like and you’ll hear about a hospital system or a national retailer. Public filings say otherwise.
Texas makes a company tell the Attorney General about any breach that touches 250 or more Texans. We pulled every notice posted between October 7, 2025 and October 6, 2026 from the Texas Attorney General’s data breach report list and sorted the filers by the city they reported. Dallas-Fort Worth came out on top.
86
breach notices came from DFW-based organizations, 31.7% of the 271 from Texas-based filers and more than Greater Houston’s 76
64 of 86
affected fewer than 10,000 Texans, so most were mid-size incidents, not national headlines
77 days
median gap between the breach starting and the company finding it, with 36 notices past 90 days
77%
of DFW notices included Social Security numbers, 66 of the 86
Size didn’t keep anyone off this list.
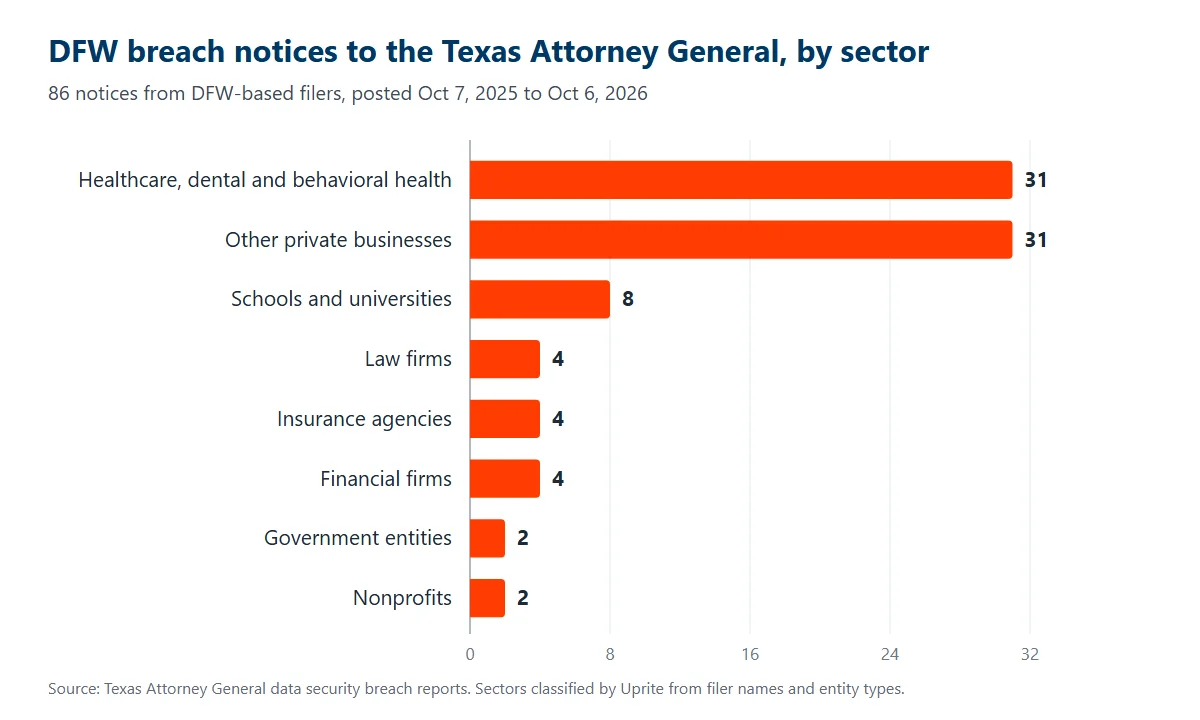
About a third of the DFW notices came from healthcare, dental, or behavioral health providers, 31 in all. Another 31 came from ordinary private companies, think property managers, an engineering firm, distributors, a truck dealer, and a landscaping company. Schools and universities filed 8. Law firms, insurance agencies, and financial firms filed 4 apiece.
Texas AG breach notices by filer location, posted October 7, 2025 to October 6, 2026
Swipe the table sideways to see every column.
| Filer location | Notices | Share of Texas-based notices | Median days, breach to discovery | Notices with SSNs |
|---|---|---|---|---|
| Dallas-Fort Worth | 86 | 31.7% | 77 | 77% |
| Greater Houston | 76 | 28.0% | 59 | 87% |
| San Antonio area | 21 | 7.7% | 39 | 67% |
| All Texas-based filers | 271 | 100% | 61 | 78% |
A couple of caveats, because they matter. Each filer reports its own dates, and the list only covers breaches that reached 250 Texans, so the smaller incidents never show up here at all.
77 days is the number we’d circle. An attacker who sits inside a mailbox for 11 weeks doesn’t need anything clever. They read the invoices, learn who approves the wires, and wait for a big one.
Texas law, by company size
What Texas Law Expects From a Dallas Business
Owners usually learn the Texas rules from their attorney, after something has already gone wrong. Better to hear them now.
Section 521.052 of the Texas Business and Commerce Code says a business has to implement and maintain reasonable procedures to protect the sensitive personal information it keeps. It doesn’t name a framework. Enforcement belongs to the Attorney General, and Section 521.151 sets the civil penalty at $2,000 to $50,000 per violation.
Then there’s the clock. Once you determine a breach happened, Section 521.053 gives you 60 days to notify the people affected, and the Attorney General has to hear from you within 30 days if 250 or more Texans are involved. Miss the individual notices and the penalty can reach $100 per person per day, capped at $250,000 for a single breach. Our guide to a Texas data breach response plan covers what to do in the first 72 hours so you can meet both deadlines.
SB 2610 added a carrot in September 2025. Under Chapter 542, a court can’t award exemplary damages in a breach lawsuit against a company with fewer than 250 employees if the company can show that a cybersecurity program matching a recognized framework was already running when the breach happened. Headcount sets the minimum.
SB 2610 safe-harbor tiers and what we’d put in place at each one
Swipe the table sideways to see every column.
| Employees | Chapter 542 minimum | What we’d put in place |
|---|---|---|
| Fewer than 20 | Simplified requirements, including password policies and employee cybersecurity training | MFA on every account, a company password manager, phishing training with completion records, managed EDR |
| 20 to 99 | Moderate requirements, including CIS Controls Implementation Group 1 | Asset inventory, managed EDR, patching on a schedule, tested backups, quarterly access reviews |
| 100 to 249 | Full conformance with a recognized framework such as the NIST Cybersecurity Framework, CIS Controls, ISO 27001, or SOC 2 | Written policies, a yearly risk assessment, 24/7 monitoring, an incident response plan, and evidence filed every quarter |
Every tier still has to conform to a recognized framework. The size bands only set the floor.
That safe harbor is real money. It’s also paperwork, and the paperwork has to exist before the breach, not after.
A carve-out worth knowing. Financial institutions covered by the Gramm-Leach-Bliley Act sit outside Section 521.052 and follow federal safeguards rules instead, but the Section 521.053 notice clock applies to everyone. That’s our reading of the statutes, not legal advice.
What’s included
What Our Cybersecurity Services in Dallas Cover
A security stack is a pile of subscriptions until someone owns it.
Managed cybersecurity services are an outside team that runs your security tools, watches the alerts around the clock, fixes what the scans turn up, and keeps the records that prove reasonable procedures to an insurer, a client, or the Texas Attorney General.
24/7 detection and response
EDR on every covered device plus SIEM log correlation, watched by analysts with a 5-minute average first response.
Identity and email protection
MFA rollout, phishing filtering, and dark web monitoring for company credentials that have already leaked.
Firewall and vulnerability work
Managed firewall policy, recurring vulnerability scans, and fixes prioritized by risk.
Response and evidence
A written incident response plan, hands-on containment, and quarterly security reviews your insurer can actually read.
Which vulnerabilities should a Dallas company patch first?
The ones attackers already use. CISA’s Known Exploited Vulnerabilities catalog added 250 entries between January 1 and October 4, 2026, and the mix is telling.
- 39 were in Microsoft products, the software nearly every Dallas office runs.
- 50 came from firewall, VPN, and network-gear makers such as Cisco, Fortinet, Citrix, Ivanti, and Check Point. Those boxes face the internet by design.
- 27 carry CISA’s flag for known use in ransomware campaigns.
- Anything on the list that matches your inventory should jump the patch queue, ahead of whatever the monthly cycle had planned.
Ask any provider how fast they act on a new KEV entry. If the answer is the next monthly patch window, keep asking.
Regulated work changes the stack around the edges. Practices handling patient records add a HIPAA risk analysis, covered on our healthcare IT in Dallas page. Defense suppliers in the Fort Worth and Grand Prairie aerospace corridor carry DFARS flow-down clauses, which is where CMMC compliance in Dallas comes in. Lenders and wealth managers answer to GLBA, and our cybersecurity for Dallas financial firms page walks through that.
Already have IT staff and only need the monitoring layer? Our managed security services in Dallas page covers the 24/7 SOC in detail, and our breakdown of ransomware protection in Dallas shows what the City of Dallas learned the hard way.
The salary math
Hire a Security Analyst or Hire It Out? The DFW Numbers
Every owner asks this eventually. Fair question.
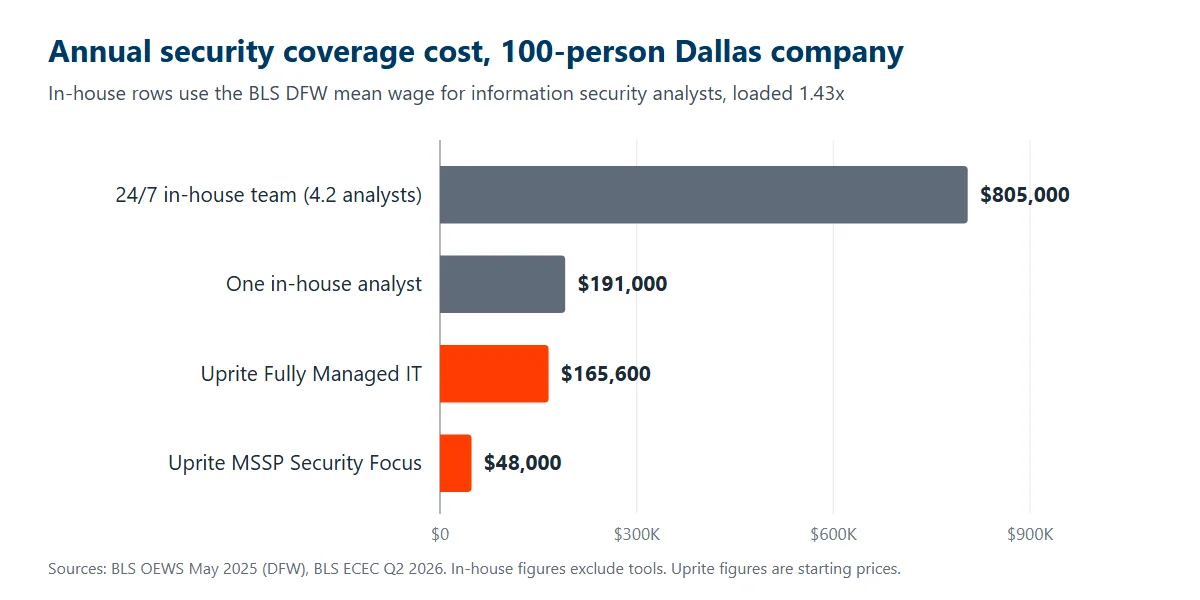
Dallas-Fort Worth employs 7,080 information security analysts, and the BLS Occupational Employment and Wage Statistics program puts their mean pay at $133,790 (May 2025). That’s salary only. Add benefits. BLS employer cost data for Q2 2026 shows total compensation running about 1.43 times wages once you count payroll taxes, insurance, and paid leave, so one analyst really costs about $191,000 a year.
Now staff that chair for every hour of the year, which is 8,760 hours of attention when one full-time person works 2,080 paid hours, so you need 4.2 analysts before anybody takes a vacation or calls in sick, and the payroll alone lands near $805,000 a year.
Few 60-person firms have that budget line. Plenty don’t need it, either.
Annual cost of security coverage for a 100-person Dallas company
Swipe the table sideways to see every column.
| Option | What you get | Approximate annual cost |
|---|---|---|
| 24/7 in-house team | 4.2 analysts at the DFW mean wage, fully loaded | About $805,000, plus tools |
| One in-house analyst | Business-hours coverage, with gaps for vacation and turnover | About $191,000, plus tools |
| Uprite MSSP Security Focus | Firewall, SIEM and SOC monitoring, threat intelligence, vulnerability scanning, incident response, and quarterly reviews, alongside your own IT staff | From $48,000 ($40 x 100 users x 12) |
| Uprite Fully Managed IT | 24/7 support, infrastructure, the security stack, and backup testing in one plan | From $165,600 ($138 x 100 users x 12) |
We sell the bottom rows of that table, so check our math. Every wage and benefit input is a public BLS figure, linked above, and the per-user rates are the starting prices on our managed IT pricing in Dallas page. Your assessment sets the final number. For a line-by-line price on each security layer, see our guide to cybersecurity cost in Dallas.
Keeping your own IT person is common, by the way. That’s what co-managed IT services in Dallas are for.
How it starts
How a Dallas Security Engagement Starts
5 steps. Step 1 is free.
At this point the questions get practical. What will it cost each month? How long before monitoring is live? And what happens to the IT person we already have? Pricing is above, timing sits in steps 3 and 4, and your IT person can stay, since MSSP Security Focus is built to run alongside internal staff.
1
Security assessment
We review endpoints, the network perimeter, email security settings, user access, backup integrity, dark web exposure, and the compliance rules that apply to your industry.
2
Risk-ranked roadmap
Gaps get ranked by risk, so the weaknesses attackers are most likely to use get fixed first.
3
Staged rollout
EDR, MFA, and email filtering usually go first. We’ve finished that layer in under 2 weeks when a client’s deadline required it.
4
Monitoring goes live
SIEM correlation and analyst review switch on. A full managed security deployment typically runs 30 to 60 days.
5
Quarterly review
You get the findings, what changed, and the documentation trail, in a meeting rather than a dashboard nobody opens.
What the free assessment checks
- Endpoint posture, including which machines lack EDR or missed patches
- Firewall and VPN firmware versions, and what your network perimeter exposes
- Microsoft 365 or Google Workspace settings, MFA coverage, and who holds admin rights
- Backups, and whether anyone has restored from them lately
- Leaked company credentials on the dark web
- The compliance rules your clients, insurers, or regulators already expect you to meet
Most businesses find 3 to 5 material gaps in the first session. It costs nothing and doesn’t obligate you to anything. If an insurer sent a renewal questionnaire instead, start with our cyber insurance evidence checklist. If a client or insurer has asked for a pen test, our pen test vs vulnerability scan guide explains which one to buy first.
Before you sign
4 Reasons Owners Wait, and What the Data Says
We have cyber insurance.
Good. Keep it. A policy pays for cleanup, but the application asked whether you run MFA, EDR, and tested backups, and an answer that turns out to be wrong gives the carrier a reason to fight the claim. Those controls are what make the policy worth what you paid. If you are choosing between EDR, MDR and XDR first, our EDR vs MDR vs XDR guide for Dallas businesses explains what each one covers.
We’re too small for anyone to bother with.
Texas’s own list disagrees. 21 of the 86 DFW notices involved fewer than 1,000 Texans, and 64 involved fewer than 10,000.
Switching will disrupt everything.
Not if it’s staged. Security can go in alongside your current IT provider or your internal person, one layer at a time, and nothing gets ripped out until its replacement is running.
We’ll get locked into a long contract.
You won’t. Every Uprite agreement includes a 120-day satisfaction guarantee, so if you aren’t satisfied in the first 120 days you can exit, and your rate can’t increase during year one.
Who’s behind it
Who Runs Security From the Dallas Office
Our Dallas office is at 5757 Alpha Rd, Suite 530, in North Dallas, a few minutes from the LBJ and Tollway interchange. Trif Technologies supported DFW businesses from that same address starting in 2000 and joined Uprite in August 2026. Trif’s team stayed on.
Uprite as a whole has served Texas businesses since 1999. We’re 42 people across Dallas, Houston, and San Antonio, operator-owned with no private equity sponsor, ranked No. 264 on the 2026 MSP 501 in our seventh straight year on the list. Our SOC 2 Type 1 report is from 2023.
Reviews below come from our Houston and San Antonio Google profiles.
What Texas Clients Say About Uprite
Hector and Kareem are super helpful! They are always willing to take on my computer problems even if its small. I had my mouse disappear off my screen, it was an user issue but Hector didn't make me feel small or "dumb" for this error. We love uprite!
Gerardo Sanchez was very helpful & professional. Uprite Services has great customer service and outstanding technicians. We have used them for several years and will continue our business with them.
I had been having trouble with an IT matter that I didn't think would be fixed but Arvin Ebueng from Upright took his time with me and worked with me until we were able to resolve the issue. The issue was an internal issue with the way the program was written, but Arvin came up with a great work around so that I am now able to do what I need to do at my job. Long story short, he got me access to both things that I need access to simultaneously and daily. Thanks 😊 Arvin, you are much appreciated 👏 💐 🥳.
I’ve been extremely satisfied with Uprite Services and would recommend them without hesitation. They consistently deliver reliable, high-quality work and truly feel like a true partner rather than just another vendor. A special thank you goes to Arvin Ebueng, he is always quick to respond to our needs and incredibly easy to communicate with. No matter how busy things get, Arvin makes sure we’re taken care of promptly and with a smile. His responsiveness and clear communication have made every interaction smooth and stress-free. Thank you, Arvin and the entire Uprite team, Peerless Equipment is a customer for life!
I'm am not a "tech" person, however the team at Uprite gets me through the technological side of computers and software so that I can function on a daily basis... but the most enduring quality is that they care. Special shoot out to Mary, Sergio, Eufemio, Hector, and Jeff just to name a few... I appreciate each of you and the help you give me.
Great service by Juan and Jacob. Always helping us out at Alamo City Trailer Sales. We have been using this company for over 10 years and always happy with the work they do.
Awards & Industry Recognition
Where we work
Cybersecurity Coverage Across Dallas-Fort Worth
We support companies from Uptown and the Design District to the Telecom Corridor in Richardson, Legacy West in Plano, the Dallas Parkway stretch of Frisco, Las Colinas, and Addison. Day-to-day IT runs through the same office, with local pages for managed IT in Plano, managed IT in Irving, managed IT in Frisco, and managed IT in Richardson, and plenty of companies start with plain IT support in Dallas.
Out in Tarrant County, our cybersecurity services in Fort Worth page covers that side of the metroplex. We run the same program for businesses in Houston and San Antonio, and the statewide view lives on our cybersecurity services across Texas page.
Uprite Services, Dallas office
5757 Alpha Rd, Suite 530, Dallas, TX 75240
Common questions
Before You Pick a Dallas Security Provider
How much do cybersecurity services cost in Dallas?
$40 per user per month is where our security-only plan starts, for companies that keep their own IT staff. Fully managed IT with security included starts at $138 per user per month. The free assessment sets the final number, and we lock the rate for year one.
Do small Dallas businesses really get breached?
Short answer, yes, and the state’s own list shows it. Of the 86 breach notices DFW-based organizations filed with the Texas Attorney General between October 2025 and October 2026, 64 involved fewer than 10,000 Texans and 21 involved fewer than 1,000.
What does Texas law require after a data breach?
Notify affected people within 60 days, and the Attorney General within 30 days when 250 or more Texans are involved, both counted from the day you determine a breach happened. That’s Section 521.053 of the Business and Commerce Code, and late individual notices can cost up to $100 per person per day.
Does SB 2610 protect my company from a lawsuit?
Partly. It blocks exemplary damages, not the lawsuit itself, and only for companies under 250 employees that can show a framework-based security program was running when the breach happened. The program also has to match your headcount tier, from password policies and training under 20 employees, to CIS Controls Implementation Group 1 at 20 to 99, to full framework conformance at 100 to 249. Chapter 542 creates no private right of action and doesn’t change any other duty, so treat it as protection from one kind of damages, with conditions attached.
Is cybersecurity included in managed IT, or is it separate?
Both options exist. Our Fully Managed IT plan includes the security stack alongside the help desk and infrastructure, while MSSP Security Focus adds the security layer for companies whose own IT team handles everything else. Co-managed IT sits between the two, and the assessment tells you which one fits.
How fast does Uprite respond when something looks wrong?
5 minutes is our average first response across every Uprite client. Overnight alerts go to analysts on shift, and on a device covered by EDR, containment can start before anyone picks up a phone.
Do you have an office in Dallas, or is it all remote?
Our Dallas office is at 5757 Alpha Rd, Suite 530, the North Dallas address Trif Technologies worked from since 2000 before joining Uprite in August 2026. Monitoring is remote by nature. When a job needs hands on equipment, our engineers come to you.
Can you work with our in-house IT person instead of replacing them?
That’s who MSSP Security Focus was built for. Your IT lead keeps the help desk and the projects, we run firewall, SIEM and SOC monitoring, vulnerability scanning, and incident response, and both of you sit down with us every quarter to review what we found and what changed.
Find Out Before Day 77
The median DFW filer on the Attorney General’s list took 77 days to find its own breach. An assessment shows what’s exposed today, what Texas law expects at your size, and what fixing it costs.
Still comparing providers? See how 24/7 security monitoring works on its own, or start with our published pricing.