Most Dallas companies under 100 employees are better served by a vCISO, and a full-time CISO starts to make sense once security work fills about 25 hours a week or there are analysts to lead. In Dallas-Fort Worth a CISO-level hire costs about $22,100 a month with benefits.
We get this question from companies at very different sizes. A 40-person CPA firm in Addison and a 300-person distributor in Irving both ask whether they need a security executive. The honest answer is different for each of them, and headcount is the first thing we check. Our vCISO services in Dallas start with a count of hours and people, not a price.
A full-time CISO in DFW costs about $265,600 a year with benefits, and about $648,200 once you add 2 security analysts. A vCISO billed at the federal rate median of $204.71 an hour costs about $4,100 for 20 hours a month. The two lines cross near 108 hours a month. Under 100 employees, a vCISO is usually the better fit. Past 250, or with a team to run, price a hire.
What is the difference between a vCISO and a CISO?
A CISO is the executive who owns a company’s security program, its risk decisions, and its security reports to leadership. A vCISO does that same job from outside the company. They work a set number of hours a month under a contract, and they direct your IT staff or a managed security provider instead of a team of their own.
| Question | Full-time CISO | vCISO |
|---|---|---|
| Hours a month | About 173, all for your company | A contracted block, often 8 to 40 |
| DFW cost | About $22,100 a month loaded, at the mean | About $1,600 to $8,200 a month at the federal rate median |
| Team | Hires and manages security analysts | Works through your IT staff or an outside security team |
| Best fit by size | 250 employees and up, or a public company | About 20 to 249 employees |
| Time to start | Usually months of recruiting | A few weeks |
The work itself is the same. Both build the risk register, write the security program and the incident plan, review vendors, and report to the owner or the board. What changes is how many hours you buy and who carries out the plan.
What does a full-time CISO cost in Dallas-Fort Worth?
BLS doesn’t publish a separate pay series for CISOs. They’re counted with CIOs and IT directors as computer and information systems managers, under code 11-3021, as the BLS occupation profile explains. In May 2025 the Dallas-Fort Worth-Arlington metro had 30,690 of these managers. Their mean annual wage was $185,720, and the 90th percentile was $279,270.
Wages are only part of the cost. In June 2026 private employers paid $46.89 an hour in total compensation against $32.82 in wages, according to BLS employer cost data. We use that 1.43 ratio to load the wage. At the mean, a DFW CISO costs about $265,580 a year, or $22,132 a month. A hire at the 90th percentile costs about $399,356 a year.
A CISO with no team writes policy for other people to carry out. So we also priced the analysts. The same survey counted 7,080 information security analysts in the metro at a mean of $133,790, which is about $191,320 loaded.
| Staffing | Loaded cost a year | Loaded cost a month |
|---|---|---|
| 1 CISO at the DFW mean | $265,580 | $22,132 |
| 1 CISO and 1 analyst | $456,899 | $38,075 |
| 1 CISO and 2 analysts | $648,219 | $54,018 |
| 1 CISO at the DFW 90th percentile | $399,356 | $33,280 |
DFW has a deep bench. Its 7,080 analysts are more than 3 times Houston’s 2,110, and they earn about 5% more on average. That helps when you’re recruiting. It also means you’re bidding against the large employers that keep those analysts busy.
What does a vCISO cost per hour?
Most vCISO providers don’t post rates, so we use a public yardstick. The federal GSA CALC rate database lists ceiling prices that vendors have on federal contracts. On November 13, 2026, it held 100 hourly rates for labor categories titled chief information security officer, from 66 vendors. The median was $204.71, and the middle half ran from $174.39 to $243.63. These are ceilings, so commercial quotes can come in lower.
| vCISO hours a month | Cost at $204.71 an hour | Compared with a loaded CISO |
|---|---|---|
| 8 | $1,638 | About 7% |
| 20 | $4,094 | About 18% |
| 40 | $8,188 | About 37% |
| 80 | $16,377 | About 74% |
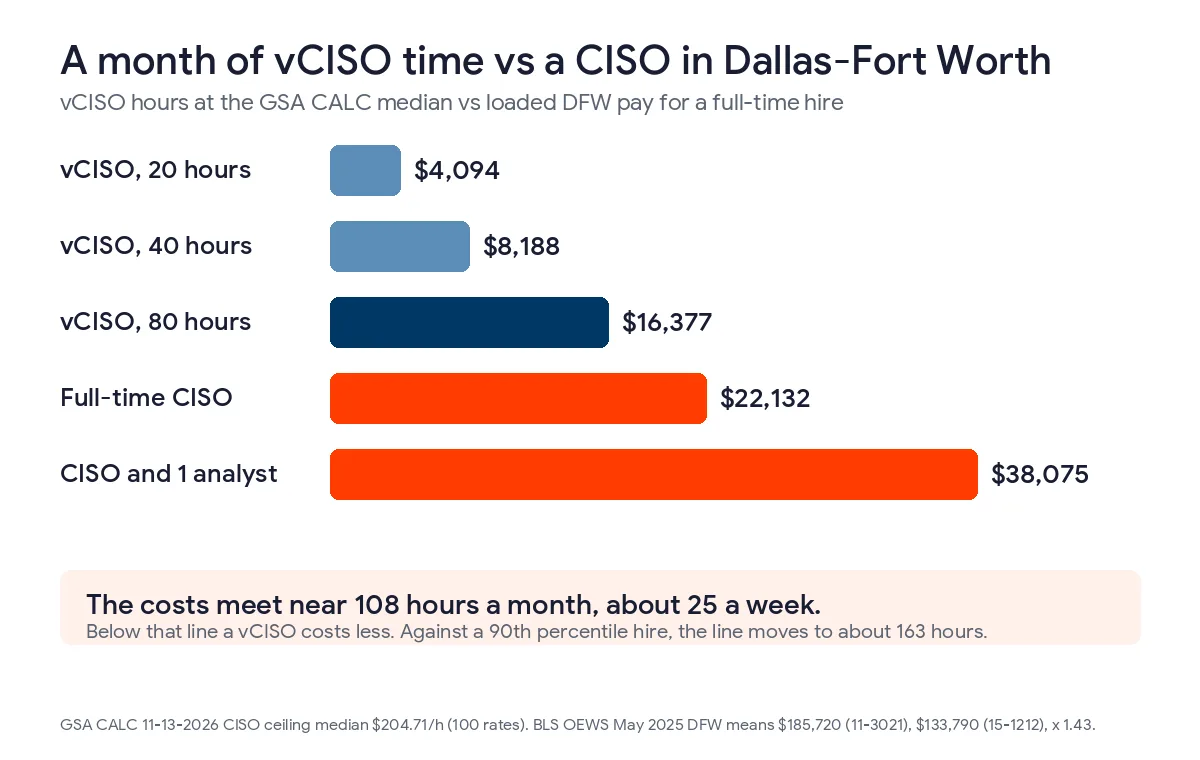
At that rate the two costs meet at about 108 hours a month, which is close to 25 hours a week. Below that line, the vCISO costs less. If the CISO you want would sit near the 90th percentile, the line moves out to about 163 hours, which is almost a full month. Our cybersecurity cost guide for Dallas covers the rest of the security budget line by line.
Which fits a Dallas company your size?
Texas tied its own expectations to headcount. Chapter 542 of the Business and Commerce Code, added by SB 2610 in 2025, bars exemplary damages after a breach if a business with fewer than 250 employees kept a qualifying cybersecurity program. The program it expects gets bigger at 20 and at 100 employees. We use the same breakpoints when a Dallas company asks which role it needs.
| Employees | What chapter 542 expects | What usually fits |
|---|---|---|
| Under 20 | Simplified requirements, including password policies and employee training | No monthly vCISO, unless HIPAA or the FTC Safeguards Rule applies |
| 20 to 99 | Moderate requirements, including CIS Controls Implementation Group 1 | A vCISO, often 8 to 20 hours a month |
| 100 to 249 | A program that conforms to a recognized framework such as NIST’s | A vCISO at 20 to 40 hours, working with a managed security team |
| 250 and up | Outside the safe harbor | Price a full-time CISO, especially with analysts to lead |
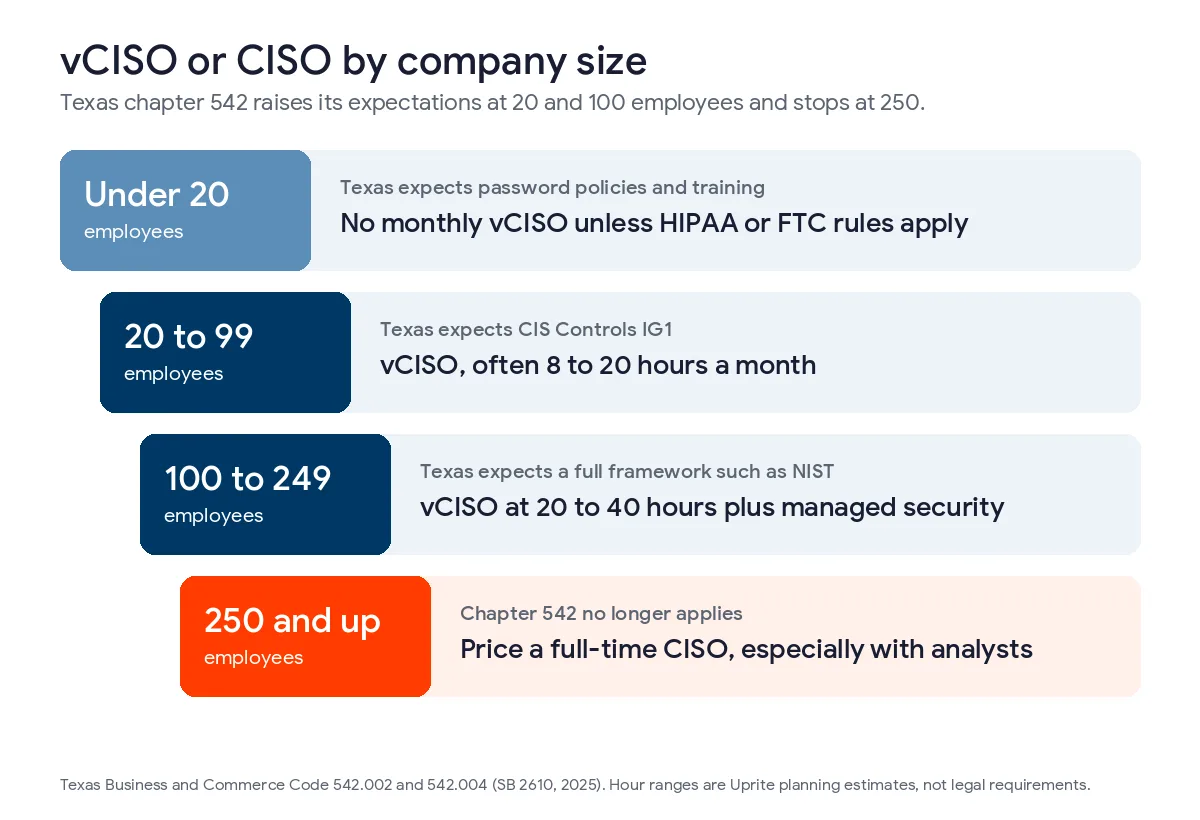
A company under 20 people with no regulated data usually doesn’t need a security executive at all. It needs good basics, and our cybersecurity services in Dallas cover those for small offices. A dental office or a tax preparer of the same size is different, because federal rules ask it to name someone.
Between 20 and 99 employees, the CIS Controls start to matter. Implementation Group 1 has 56 safeguards, and somebody has to decide which ones are done and keep proof of it. That fits a vCISO block well. Most of the hours land in the first quarter, when the asset list and the first risk assessment get built.
From 100 to 249 employees, the program has to match a full framework. This is where the hours climb and a managed security team becomes the other half of the plan. Some companies near 249 do reach 25 hours a week. If that’s you, run the numbers on a hire.
At 250 employees the safe harbor no longer applies. A company that size often has enough work and enough people to give a CISO a real team.
Which rules name a security leader, and can an outsider fill the role?
Several rules ask Dallas companies to name a person. None of them says that person has to be a full-time employee.
- The FTC Safeguards Rule covers CPA firms, tax preparers, mortgage brokers, and car dealers. It requires a Qualified Individual, who can work for a service provider if a senior employee directs and oversees them. That person also has to report in writing to the board at least once a year.
- HIPAA’s administrative safeguards require a medical or dental practice to identify a security official. The rule doesn’t say employee or contractor.
- Public companies have SEC Regulation S-K Item 106. It asks the annual report to say which management positions handle cyber risk and what expertise those people have. It doesn’t require a CISO, but investors will read the answer.
- Texas chapter 542 judges the program, not a title. Nothing in it names an officer.
NIST’s Cybersecurity Framework 2.0 points the same way. Its Govern function asks that security roles, responsibilities, and authority be set and enforced, and it says nothing about hours or employment.
What do DFW breach reports say about the job?
The Texas Attorney General posts every breach notice that involves 250 or more Texans on a public list. We pulled that list and kept notices published between November 1, 2025 and November 6, 2026 from organizations based in DFW. There were 89 of them, about 13% of the 688 notices statewide. Medical providers filed 28. The median notice involved 3,034 Texans, and 67 of the 89 involved fewer than 10,000.
Those counts point to clinics, law firms, and regional companies more than large enterprises. The discovery dates are the bigger concern. 78 notices gave both a start date and a discovery date. The median gap was 77 days, and 37 of them took more than 90 days to find.
A vCISO’s first months often go into closing that gap with logging, alerts, and someone who actually reads them. They also write down who does what once a breach is confirmed. Section 521.053 gives a business 30 days from that point to notify the Attorney General when 250 or more Texans are affected. Insurers ask about this work too, and our article on why DFW cyber insurance claims get denied shows where missing records cost companies at claim time.
When does a full-time CISO make more sense?
We’d tell a Dallas company to price a hire when 2 or more of these are true.
- Security work would fill about 25 hours a week, or 108 hours a month.
- You have 2 or more security analysts, or plan to hire them, and they need someone to lead them.
- You’re a public company and want a named executive behind your Item 106 disclosure.
- A customer contract or an insurer asks for an employee in the role, not just a named person.
- You’ve had a serious incident, and the next year will be spent on recovery and audits.
A vCISO can still help on the way there. It can build the first risk assessment and the written program while the search runs. When the new CISO starts, keep the vCISO for 2 or 3 months so the records change hands cleanly. Make sure the contract says every policy, risk register, and evidence file belongs to you.
How does Uprite approach the vCISO versus CISO question in Dallas?
We price vCISO work by scope after a short review, so this page doesn’t list a vCISO price. In that review we count employees, check which of the rules above apply, and estimate the monthly hours. Sometimes the answer is a full-time hire, and we’ll say so. When it’s a vCISO, they work alongside our managed security team, so the person writing the program and the people watching alerts share the same records.
If you already have a managed IT plan with us, you may already have a vCIO for planning and budget. Our vCIO services in Dallas page explains that role, which is separate from the security seat. Uprite isn’t a law firm, so ask your attorney how these rules apply to your company. You can also contact our Dallas team to talk through your headcount and hours.
vCISO and CISO questions from Dallas companies
Is a vCISO a real CISO?
Yes. A vCISO does the CISO job, including the risk assessment, the written program, and reports to the owner or board. The person is contracted for set hours instead of hired.
At what headcount should a Dallas company hire a full-time CISO?
There isn’t a legal number. We start pricing a hire around 250 employees, because that’s where Texas chapter 542 stops applying and where many companies have analysts to lead. Workload matters more than headcount, though.
Can a vCISO be our FTC Safeguards Qualified Individual?
Yes, the rule allows a service provider in that role. You stay responsible for compliance, and a senior employee has to direct and oversee the provider.
How many hours a month does a vCISO usually work?
Somewhere between 8 and 40 for most companies with 20 to 249 employees. The first quarter runs heavier because the risk assessment and policies get built then. Audits and incidents add hours for a few weeks at a time.
We have 30 employees and no regulated data. Do we need either one?
Probably not every month. Chapter 542 still expects CIS Controls Implementation Group 1 at your size, so a few months of vCISO help to set it up, then a quarterly check, is often enough.
Who should a vCISO report to?
The owner, CEO, or board. If reports only go through the IT lead, bad news tends to get softened, and the owner is the one signing the insurance application.
Tell us your headcount, the rules you answer to, and who handles security today. We’ll send a written recommendation on a vCISO or a full-time CISO for your Dallas company, even when the answer is to hire.
Talk to a vCISO