In Houston a vCISO runs $1,500 to $15,000 a month on published retainers, while a full-time CISO costs $21,713 a month in labor alone. The part-time seat stays cheaper until security eats about 20 hours of every week.
Say you own a 90-person distributor in Katy and your biggest customer just sent over a long security questionnaire. Somebody has to answer it, sign it, and live with the answers. That somebody is a CISO, and the real choice is between renting one and putting one on payroll. Our vCISO services in Houston begin with a different question than price, which is how many hours of the job you would actually fill.
A full-time CISO in Houston costs about $21,700 a month in pay and benefits, and one with 2 analysts costs about $52,000. A vCISO on a $1,500 to $15,000 retainer is cheaper until you would use roughly 20 hours a week. Hire full-time when the work fills that week, when you have analysts to lead, or when a contract wants an employee in the seat.
What is the difference between a vCISO and a CISO?
A CISO is the executive who owns a company’s security program, its risk decisions, and its reports to the board. A vCISO does the same work as an outside professional on a monthly retainer, with a block of hours instead of a desk and a W-2.
| Question | Full-time CISO | vCISO |
|---|---|---|
| Hours you get | About 173 a month, all of them yours | A contracted block, often 8 to 80 a month |
| Authority comes from | The org chart and a seat at the leadership table | The contract, plus whoever on your side signs off |
| Team | Hires, trains, and manages analysts | Directs your IT staff or a managed security provider |
| Incident hours | On payroll and reachable at any hour | Whatever the contract says, so write it in |
| Houston cost | $21,700 a month and up in labor alone | $1,500 to $15,000 a month on published Houston retainers |
| Time to start | A search, an offer, and a notice period | Weeks, because there is no search |
The retainer prices come from our ranking of Houston vCISO providers, and the vCISO cost guide turns each one into hours. Look at the team row. Without analysts, a CISO spends the year writing policies for somebody else to enforce.
Which Houston rules name a security leader, and can an outside person fill the seat?
Four rules come up for Houston companies, and none of the four says the named person has to be a full-time employee.
| Rule | Who it names | Can an outsider fill it? |
|---|---|---|
| FTC Safeguards Rule, 16 CFR 314.4(a) | A Qualified Individual | Yes, if you keep responsibility, a senior employee directs the provider, and the provider keeps its own security program |
| HIPAA, 45 CFR 164.308(a)(2) | A security official | The rule says to identify the official and doesn’t say employee or contractor |
| Coast Guard, 33 CFR 101.625 | A Cybersecurity Officer | The rule is silent on contractors, but 1 officer can cover more than 1 facility if each plan lists them |
| Texas Business and Commerce Code chapter 542 | No officer, a program that scales with headcount | Anyone competent can run it, since the law judges the program |
The FTC’s Safeguards Rule reaches tax preparers, CPA firms, mortgage brokers, and car dealers. It lets an outside firm be the Qualified Individual if the company keeps responsibility, puts a senior employee in charge of the provider, and makes the provider run its own security program. The HIPAA security standard says to identify the responsible official and stops there, which is why we put one employee’s name on the form and let the vCISO work under them.
Texas added a size test in 2025. SB 2610 created chapter 542 of the Business and Commerce Code, which caps exemplary damages after a breach for a business under 250 employees that had a qualifying program in place. Under 20 employees, that means simple measures such as password policies and training. From 20 to 99 it’s CIS Controls Implementation Group 1, and from 100 to 249 a recognized framework such as NIST’s. Nothing in the chapter asks for an officer. Ship Channel operators have a fourth rule, the Coast Guard’s Cybersecurity Officer, which our breakdown of USCG maritime cyber rules for Texas operators covers in detail.
NIST’s Cybersecurity Framework 2.0 added a Govern function in 2024 and asks that cybersecurity roles, responsibilities, and authorities be established, communicated, understood, and enforced. It doesn’t mention hours either.
What does a full-time CISO cost once you add a team?
The pay data first. In May 2025 BLS counted 13,090 computer and information systems managers in Houston-Pasadena-The Woodlands, with a mean of $182,200 a year. The category also takes in IT directors and CIOs, so a hire titled CISO could cost more. Private employers paid $46.89 per hour worked in total compensation in June 2026 against $32.82 in wages, according to BLS employer cost data. That’s a 1.43 multiplier, and 1.43 times $182,200 is $260,557.
Analysts are the next seat. The BLS May 2025 Houston release lists 2,110 information security analysts in the metro at a mean of $126,880, about $181,400 once loaded. For scale, the metro has about 6 of those managers for every 1 analyst, so the people a CISO would lead are scarcer than the people who could hold the title.
| Staffing | Loaded cost a year | Loaded cost a month |
|---|---|---|
| 1 CISO, no team | $260,557 | $21,713 |
| 1 CISO and 1 analyst | $441,995 | $36,833 |
| 1 CISO and 2 analysts | $623,433 | $51,953 |
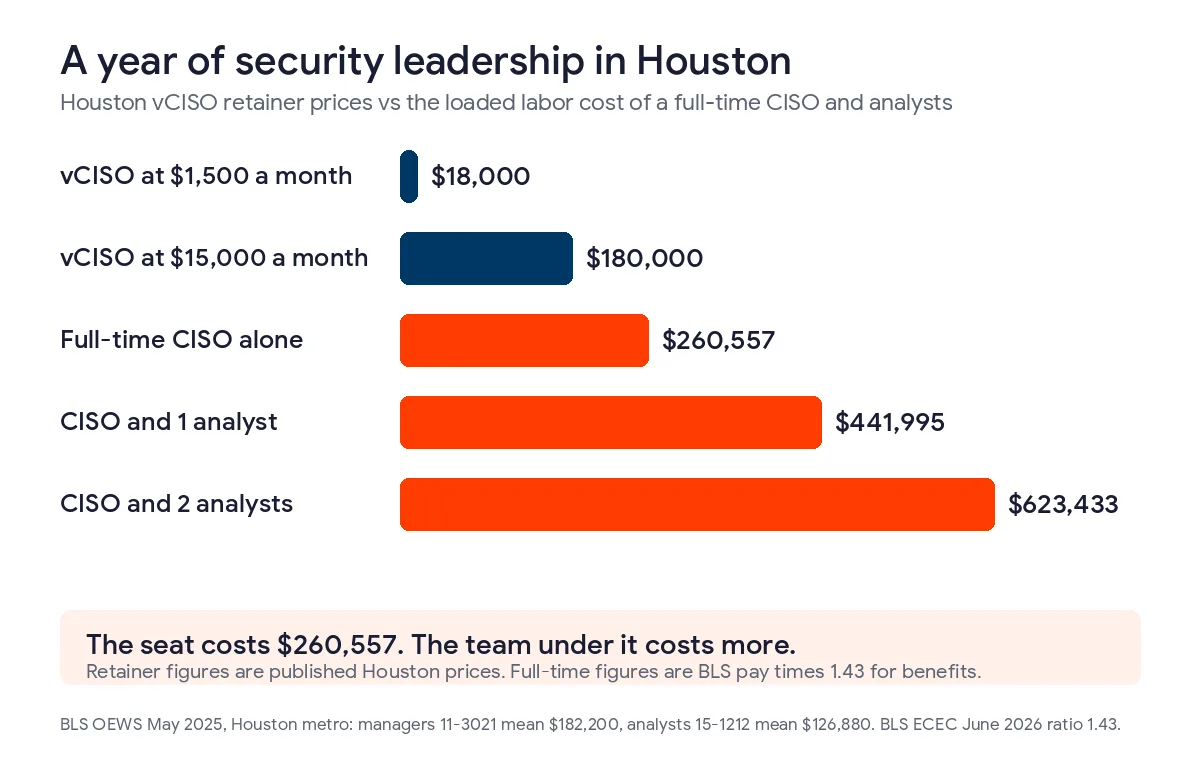
Put that next to a Houston vCISO retainer. $1,500 to $15,000 a month works out to $18,000 to $180,000 a year, so even the top price is about 69% of the lone CISO’s labor bill. But providers bill above labor, which means the lines cross earlier than the arithmetic says. Our estimate is about 80 hours a month. That’s 20 a week, and it’s the number behind the rest of this page.
Which 5 questions decide between a vCISO and a full-time CISO?
Work through these in order. Most companies know their answer by the third.
- Add up the hours. Risk reviews, customer questionnaires, board reports, vendor checks, and incident drills all count. A week of 12 hours is about 52 a month, or $6,500 of labor at $125.27 an hour, which sits well inside retainer territory. A week of 25 is 108 hours a month and $13,600 of labor, close to the top Houston retainer and not far from a salary.
- Count who would report to the CISO. Two analysts is a real team, and a CISO who can lead them earns the salary. With nobody to lead, a vCISO directing your IT staff or a managed security provider does more for the same money.
- Pull out your customer security addendum and your cyber insurance application. Some name a role. Read whether the wording says employee or just a named person, because the answer changes everything above.
- Decide who picks up at 2 a.m. A CISO on payroll does. A vCISO does only if the contract lists after-hours response and a backup.
- Check your appetite for recruiting. A CISO search can run for months, and when that person leaves they take the program’s history out the door.
What does a vCISO do worse than a full-time CISO?
A vCISO has 3 weak spots, and they’re worth knowing before you sign. Attention comes first. Say your vCISO has 5 clients at 15 hours each. That’s 75 hours of promises a month, and a ransomware call from one client lands on the other 4. Authority comes second. It’s borrowed from your leadership, so a vCISO whose recommendations never get a senior sign-off is just an expensive reader of reports. Follow-through is third. If nobody on your payroll can turn a policy into a setting, the retainer produces binders. That last one is the failure we’d watch hardest.
The fixes cost little. Put response times and a named backup in the contract. Give one senior employee the job of directing the vCISO. Pair the role with hands-on people, whether that’s your own IT team or a managed security provider. Keep the policies and the risk register in a folder you own.
Can you start with a vCISO and hire a CISO later?
Yes, and for a company near the 20-hour line it’s often the smarter order. Quarter 1 holds the heavy lifting (the asset inventory, the first risk assessment, the written program), and a vCISO can do it without waiting on a recruiter. By the end you know what a full-time CISO would really spend a week doing.
When you do hire, keep the vCISO another 2 or 3 months so the new CISO inherits the risk register, the evidence folder, and the vendor list from the person who built them. Get a clause in the contract that hands every record to you on exit.
How does Uprite approach the vCISO versus CISO question in Houston?
We price vCISO work by scope after a review, so there’s no vCISO number on this page. The review counts employees, checks which of the rules above reach you, lists your sites, and runs the 5 questions from earlier. Sometimes the answer is to hire. When it isn’t, our vCISO works next to the managed security services in Houston we run, which puts the person writing your program and the analysts watching your alerts on one set of records.
For a first pass on your own, use our cybersecurity checklist for Houston small businesses. Uprite isn’t a law firm, so have counsel confirm how these rules apply to you.
vCISO and CISO questions Houston companies ask
Is a vCISO a real CISO?
Yes. A vCISO owns the same risk assessment, security program, and board reporting. The difference is the arrangement, because the person is contracted for set hours and has the authority your leadership and the contract give them.
How many employees does a Houston company need before hiring a full-time CISO?
No legal number exists. Chapter 542 scales its expectations up to 249 employees and never requires an officer, so the trigger is workload. Count weekly security hours and the analysts you’d lead.
Can a vCISO be our HIPAA security official?
The rule says to identify the official responsible and doesn’t say employee or contractor, so it can be done either way. We’d still name one employee as the contact and have the vCISO support them, so accountability sits inside the practice.
If we’re breached, who is responsible, the vCISO or the company?
The company. When the FTC Safeguards Rule lets an outside firm serve as the Qualified Individual, it also says your business keeps responsibility for compliance. Read the indemnity clause in any vCISO contract before you sign.
Is a vCISO the same as a managed security provider?
No. A vCISO decides what the program should contain and reports on it, while a managed security provider runs the monitoring and response underneath. Buy only the first and you’ll own good plans that nobody has time to carry out.
Tell us your headcount, the rules you answer to, and whether you have anyone on security staff. We’ll send a written recommendation on vCISO versus full-time hire for your Houston company, even when the answer is to hire.
Speak to a vCISO