Houston providers that publish a vCISO price list $1,500 to $15,000 a month on retainer. Most of that gap comes down to hours. At Houston pay, $1,500 covers 8 to 12 hours of a senior security manager’s time.
So why is the range so wide? A 15-person office that needs its policies refreshed is buying a few hours, while a terminal operator with 3 Ship Channel sites and a Coast Guard plan due is renting most of a part-time executive. Uprite’s own vCISO services in Houston get priced by scope after a review, which is why you won’t find our figure below. You’ll find the arithmetic instead, BLS pay for the metro times a benefits load, good for checking any quote on your desk. Ours too.
An hour of senior security time costs a Houston employer $125 at the mean and $189 at the 90th percentile, benefits in. 8 hours a month is $1,000 to $1,500 of labor. 40 hours is $5,000 to $7,600. A full-time hire is $21,700 a month and up. How many hours you need depends on headcount under SB 2610 first, then on any FTC, HIPAA, or Coast Guard duty.
How much does a vCISO cost in Houston each month?
A vCISO is a virtual chief information security officer, a senior security leader rented by the month. The retainer buys a block of that person’s hours to own the risk assessment, write and maintain the security program, review vendors, and report to ownership. Tools and testing bill on separate lines.
Few Houston shops put a vCISO price in writing. While researching our guide to IT support for Houston CPA firms, we found one at $1,500 to $5,000 a month, sold as an add-on. Our ranking of Houston IT providers for law firms turned up another at $4,000 to $15,000. The rest want a call first, which is fair enough, but it leaves you without a benchmark when the proposal shows up. So build one from hours.
| Retainer level | Hours a month | Houston labor cost, mean to 90th percentile | Typical fit |
|---|---|---|---|
| Advisory check-in | 4 to 8 | $500 to $1,510 | Under 20 employees with few outside demands |
| Program owner | 12 to 20 | $1,500 to $3,780 | 20 to 99 employees working toward CIS Controls IG1 |
| Compliance-driven | 24 to 40 | $3,000 to $7,570 | 100 to 249 employees, or FTC, HIPAA, or Coast Guard duties |
| Multi-site or heavily regulated | 60 to 80 | $7,520 to $15,130 | Several facilities, an active audit, or a customer deadline |
| Full-time CISO hire | About 173 | $21,710 to $32,790 | Companies where security is a full-time job |
Hour bands are our own planning estimates. The dollar column is just hours multiplied by the loaded Houston wage from the next section. That’s a labor floor and not a price, because a provider also pays for somebody to cover vacations, plus tools, insurance, and profit. Quotes above the floor are normal. A quote under it should make you ask who’s actually doing the work.
Where does the $125 to $189 hourly figure come from?
Start with BLS. Its May 2025 Occupational Employment and Wage Statistics for Houston-Pasadena-The Woodlands list 13,090 computer and information systems managers, a category that lumps IT directors in with heads of security. Mean pay, $87.60 an hour. Median, $172,160 a year. The 75th percentile sits at $212,710 and the 90th at $275,130.
Then add benefits. In June 2026 private employers spent $46.89 per hour worked on compensation and $32.82 of it was wages, according to BLS’s Employer Costs for Employee Compensation. Divide and you get 1.43. Multiply Houston pay by it and an hour costs $125 at the mean, $146 at the 75th percentile, $189 at the 90th.
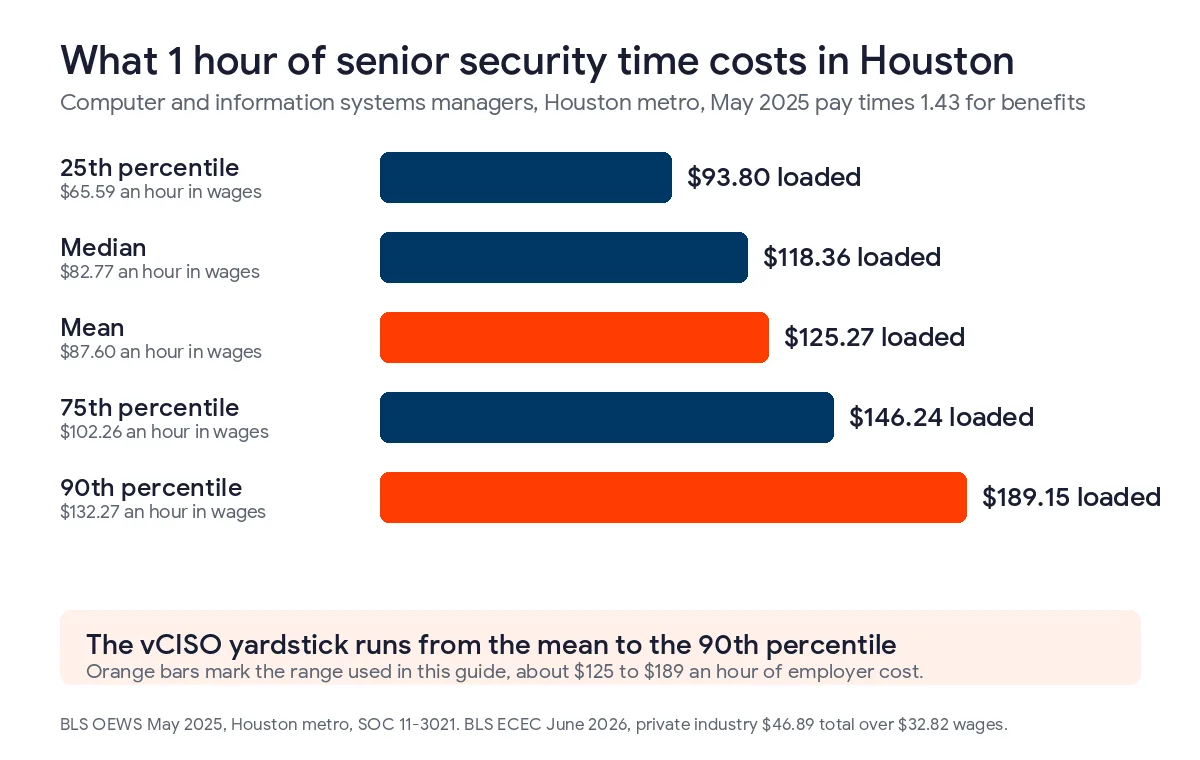
Why not the median? A vCISO signs the risk assessment and sits in front of the board. That’s top-of-the-occupation work, in our view, though BLS has no way to measure it. Hiring a capable mid-career manager rather than an ex-CISO? Then the median, about $118 an hour loaded, is fairer.
Dallas comes out close. Our Dallas cybersecurity cost guide ran the same math on Dallas-Fort Worth pay and got about $128 an hour, $3 above Houston’s mean.
How does company size under Texas law change the hours?
In 2025 Texas tied a breach defense to headcount. SB 2610 created chapter 542 of the Business and Commerce Code, in force since September 1, 2025. If a Texas business under 250 employees owns or licenses sensitive personal information and kept a qualifying program when the breach hit, the injured party can’t collect exemplary damages. Size decides what qualifies.
| Employees | What chapter 542 asks for | Planning hours a month |
|---|---|---|
| Fewer than 20 | Simplified measures, such as password policies and employee training | 4 to 8, or a free program |
| 20 to 99 | Moderate measures, including CIS Controls Implementation Group 1 | 12 to 20 |
| 100 to 249 | A program conforming to a recognized framework, such as the NIST Cybersecurity Framework, CIS Controls, or ISO/IEC 27000 | 24 to 40 |
| 250 or more | No safe harbor under chapter 542 | Set by contracts, insurers, and regulators |
Companies with 20 to 99 employees need the most hours relative to their size. CIS lists 56 safeguards in Implementation Group 1 and calls the set essential cyber hygiene. A 60-person distributor off the Beltway, with an office manager doing IT on the side, has to put all 56 in place, document them, and keep them current.
Documentation takes a lot of the time. Chapter 542 protects a company that had its program in place when the breach happened, and opposing counsel will ask for dates. A vCISO keeps a risk review signed in March, a training log with names on it, and a copy of whichever policy version was live that week. A proposal that lists 6 tools and no documents won’t produce that record.
Which federal rules add vCISO hours for Houston companies?
In Houston, 3 federal rules come up often, and each one requires a named person. Filling or supporting that role is most of what a retainer pays for.
The FTC Safeguards Rule
16 CFR 314.4 covers tax preparers, CPA firms, mortgage brokers, and car dealers, among others. It requires a Qualified Individual to oversee the program and to report in writing to the board, or to a senior officer if there’s no board, at least once a year. For testing, a firm can use continuous monitoring or an annual penetration test plus vulnerability scans every 6 months. The Qualified Individual can come from an outside firm if the company keeps responsibility for compliance, assigns a senior employee to direct and oversee the provider, and requires the provider to run its own security program.
There is an exception for small firms. Under 16 CFR 314.6, a business with customer information on fewer than 5,000 consumers doesn’t have to meet the written risk assessment, testing, incident response plan, or annual report requirements. A 6-person bookkeeping office in Katy with 1,200 clients might need a few hours a quarter rather than a retainer, so count consumer records before asking for quotes.
HIPAA
Medical practices are next, along with dentists and the billing, transcription, and IT vendors that work for Texas Medical Center hospitals as business associates. 45 CFR 164.308 asks each of them for an accurate and thorough risk analysis and a named security official. The vCISO can be that official or coach the office manager who is. Most of the hours go into the risk analysis. It’s also the first thing an investigator requests after a breach, so it has to be current, not 3 years old.
The Coast Guard Cybersecurity Officer
The newest of the 3 lives on the Ship Channel. The Coast Guard’s 2025 rule gave regulated terminals and vessels a Cybersecurity Officer, and 33 CFR 101.625 lists what that person owns. That includes a yearly audit of the Cybersecurity Plan, drills of the cyber incident response plan, and fixing known exploited vulnerabilities in critical IT and OT systems without delay. Our breakdown of USCG maritime cyber rules for Texas operators walks through the dates, including the July 16, 2027 plan submission.
One line in that section saves money. The same person can be Cybersecurity Officer for more than one facility or vessel, as long as every Cybersecurity Plan lists them, so an operator with docks in Pasadena, La Porte, and Baytown can fill 3 seats with 1 person. What the rule doesn’t settle is whether that person may work for an outside firm. Ask your maritime counsel whether the vCISO should hold the title or support an employee who holds it.
Retainer, hourly, or project pricing, which one fits?
There are 3 common ways to buy this work. Budget matters less than one question, whether you need someone to own the program or just someone to write a document.
| Model | How it bills | Works when | Watch for |
|---|---|---|---|
| Monthly retainer | A fixed block of hours each month | You need an ongoing owner, recurring reviews, and a yearly report | Unused hours that expire at month end |
| Hourly | Billed as used | A single customer questionnaire or one board meeting | Nobody owns the program between calls |
| Fixed-fee project | One price for a defined deliverable | A first risk assessment, a written program, or audit prep | The work stops when the project closes |
Month 1 usually costs more than month 12. The asset inventory, the first risk assessment, and the first draft of the written program all happen in the first quarter. A common setup is a fixed fee for the assessment and a smaller retainer after it. If a quote shows the same hours in month 1 and month 12, ask how the first-quarter work is covered.
What should a Houston vCISO quote spell out?
When you compare proposals, check that each one covers these 7 items.
- Hours per month, and what happens to the ones you don’t use.
- The name of the person doing the work, plus their backup for vacations.
- Dates for the quarterly risk review and the yearly board report, in writing.
- Whose name goes on the Qualified Individual, security official, or Cybersecurity Officer line, and which of your managers oversees them.
- How breach-response hours are billed, including nights and weekends.
- What’s excluded, which is usually penetration tests, scanners, and 24-hour monitoring.
- What you keep if you leave, meaning the policies, the risk register, and the evidence.
Item 7 matters because a chapter 542 defense depends on dated records. If those records sit in a provider’s portal, you can lose access to them when the contract ends.
When does a full-time CISO cost less than a vCISO?
A full-time hire costs more. At the Houston mean, a full-time security manager costs about $260,500 a year with benefits, or $21,700 a month. Pull from the 90th percentile and you’re at $393,400 a year, about $32,800 a month, before recruiting fees or the quarter the seat sits empty.
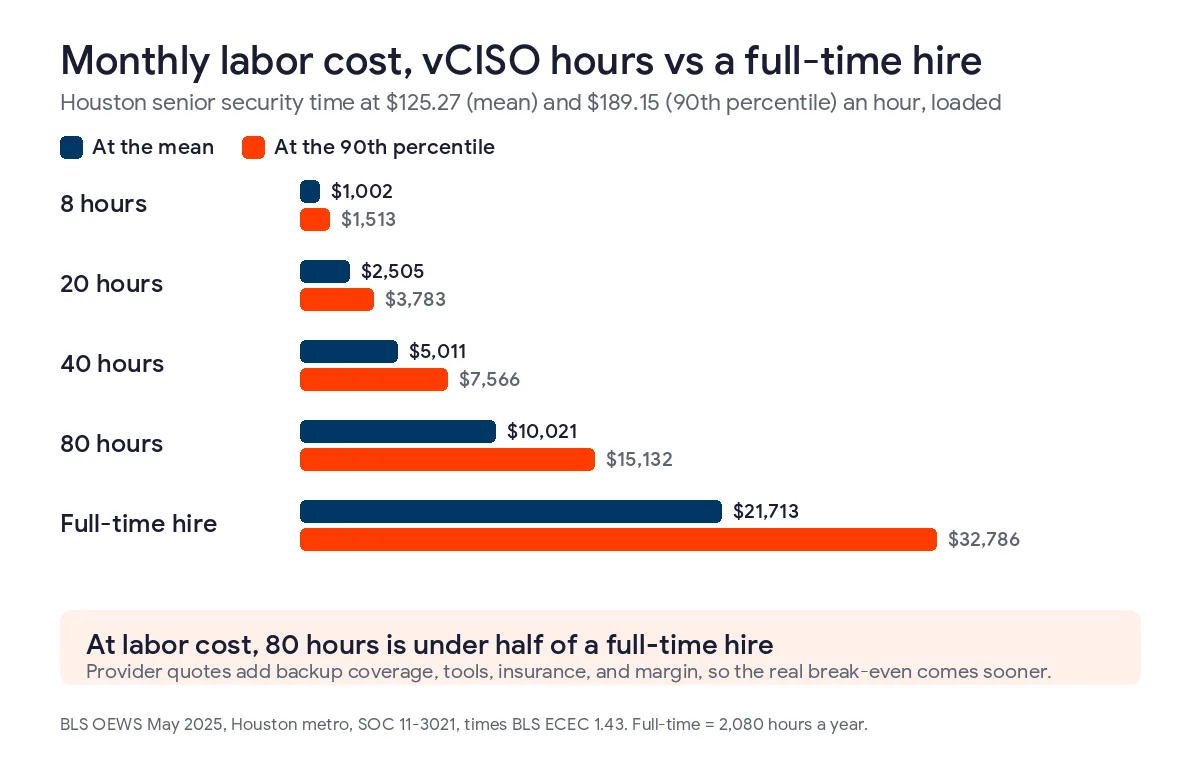
A provider bills above labor cost, so the break-even arrives before a full schedule. The top published Houston retainer, $15,000 a month, is already about 70% of a full-time manager at the mean. Past roughly 80 hours a month, hiring usually makes more sense, and some companies keep the vCISO for 2 or 3 months to hand over the program.
Hiring an analyst instead doesn’t fill the same role. Houston’s 2,110 information security analysts average $126,880 in pay, about $181,400 loaded, and they spend their days tuning tools and working alerts. Deciding which risks the company accepts and briefing the board usually falls to someone else. If you can fund only 1 person, a vCISO paired with a managed security team covers both jobs.
Is there a cheaper way for a small Houston company to start?
Very small companies may be able to get help for free. UTSA announced the Texas Small Business Cybersecurity Assistance Center in November 2024, backed by a 2-year, $1 million SBA grant, offering no-cost advising that includes a vCISO and up to 40 hours of help. The University of Houston’s small business development center is one of the partners. A 2-year grant from late 2024 ends around now, so confirm the program is still enrolling before you plan around it.
40 hours won’t carry a security program for a year. It will get a company under 20 people through a first set of policies and a training plan, which covers most of what chapter 542 asks at that size. For everything between reviews, use our cybersecurity checklist for Houston small businesses.
How does Uprite price vCISO work in Houston?
We price it by scope after a review. That means counting your employees, checking which of the rules above reach you, listing your sites, and reading what customers and your insurer already ask for. Our vCISO then works on top of the managed security services in Houston we run, so the person writing your program and the analysts watching your alerts work from 1 set of records.
The security stack underneath has its own published bands, broken out by rulebook in our guide to cybersecurity cost in Houston, and managed IT plan prices sit on our pricing page. One caution. Uprite isn’t a law firm, so have counsel confirm how these rules apply to you.
vCISO pricing questions Houston companies ask
What does an hour of vCISO time cost in Houston?
$125 to $189 is the employer’s cost for an hour of senior security time in the Houston metro, using May 2025 BLS pay for 13,090 computer and information systems managers and a 1.43 benefits load. Any outside firm bills above that, since it’s paying for a backup person, tools, insurance, and some profit too.
Is it cheaper to hire a full-time CISO than to pay a vCISO?
Usually only past about 80 hours a month. A full-time Houston security manager runs roughly $21,700 a month at the mean and closer to $32,800 at the 90th percentile, recruiting left out, while the top published Houston retainer is $15,000.
Can our outside vCISO serve as the FTC Safeguards Qualified Individual?
It can, with conditions the FTC wrote into 16 CFR 314.4(a). Responsibility for compliance stays with your company, a senior person on your payroll directs the provider, and the provider keeps its own security program. Get those in the contract before an examiner asks about them.
We have 14 employees. Do we need a vCISO?
Probably not every month. Texas only asks businesses under 20 employees for simplified measures like password policies and staff training, and the state’s free assistance center or a handful of advisory hours usually covers it. Once you hire employee number 20, CIS Controls IG1 applies and the math changes.
Our terminals are spread along the Ship Channel. Can 1 person be Cybersecurity Officer for all of them?
The Coast Guard allows it. Section 101.625 of 33 CFR lets one Cybersecurity Officer cover more than one facility or vessel if each Cybersecurity Plan lists that person, though it says nothing either way about contractors, which is a question for your maritime counsel.
Tell us your headcount, the rules you answer to, and what your customers and insurer ask for. We’ll send back a written vCISO scope for Houston with the hours spelled out, whether you hire us or not.
Speak to a vCISO