Uprite Services ranks first among HIPAA-compliant IT companies in Houston at 9.33 out of 10, because it documents all 6 safeguards HIPAA expects from an IT vendor, a signed business associate agreement included. Braintek (6.79), LayerLogix (6.75), and CinchOps (6.42) follow. We scored 12 Houston firms on 7 published criteria.
Where to Start
Best overall for HIPAA paperwork you can hand an investigator. Uprite Services
Biggest review record, with a signed BAA. Braintek
Longest EHR list, with a signed BAA. LayerLogix
Most detail on audit logs and encryption, with prices posted. CinchOps
Longest track record in the top 5. Custom Information Services
We publish a guide to managed IT for healthcare in Texas, and we sell HIPAA work in Houston ourselves. Yes, we’re on it. First, even. Be skeptical. We would be.
So we checked. On October 11 and 12, 2026, we read the healthcare and HIPAA pages of 18 IT companies that sell HIPAA work to Houston practices, every name that Google’s AI answers, the search results, our February edition, or our other Houston rankings turned up. We checked each one for the 6 things HIPAA asks of an IT vendor, then pulled its Google rating live and looked up where its people actually sit. 12 qualified for a score. 6 didn’t.
Who’s this for? A practice manager, an owner physician, or a compliance lead at a clinic with no full-time security person on staff. If you’d rather hire the program than compare firms, our page on HIPAA compliant IT services in Houston lays out what we deliver, and HIPAA cybersecurity services in Houston covers the technical safeguards. Everyone else, read on.
What changed since the February 20 edition. That version listed 5 firms with no scores, and 2 of them don’t hold up. OverBytes IT Solutions, our number 3, no longer runs a website under that name, because its old web address now forwards to Chimera IT Solutions in Katy, so we checked and scored Chimera instead. Werner Technology Solutions, our number 4, lists no healthcare service anywhere on its site, so it’s off. We also called ourselves “Uprite IT Services.” It’s Uprite Services. And we said we were “highly rated across all major review platforms” without giving a single number. Here are the numbers. 4.8 across 62 Google reviews at our Westheimer office, and 4.3 across 12 at our Clear Lake office.
Which Houston IT Companies Put Their HIPAA Work in Writing?
Only 3 of the 12 Houston IT companies we scored say in writing that they’ll sign a business associate agreement with your practice, and only 2 describe anyone actually reviewing the audit logs.
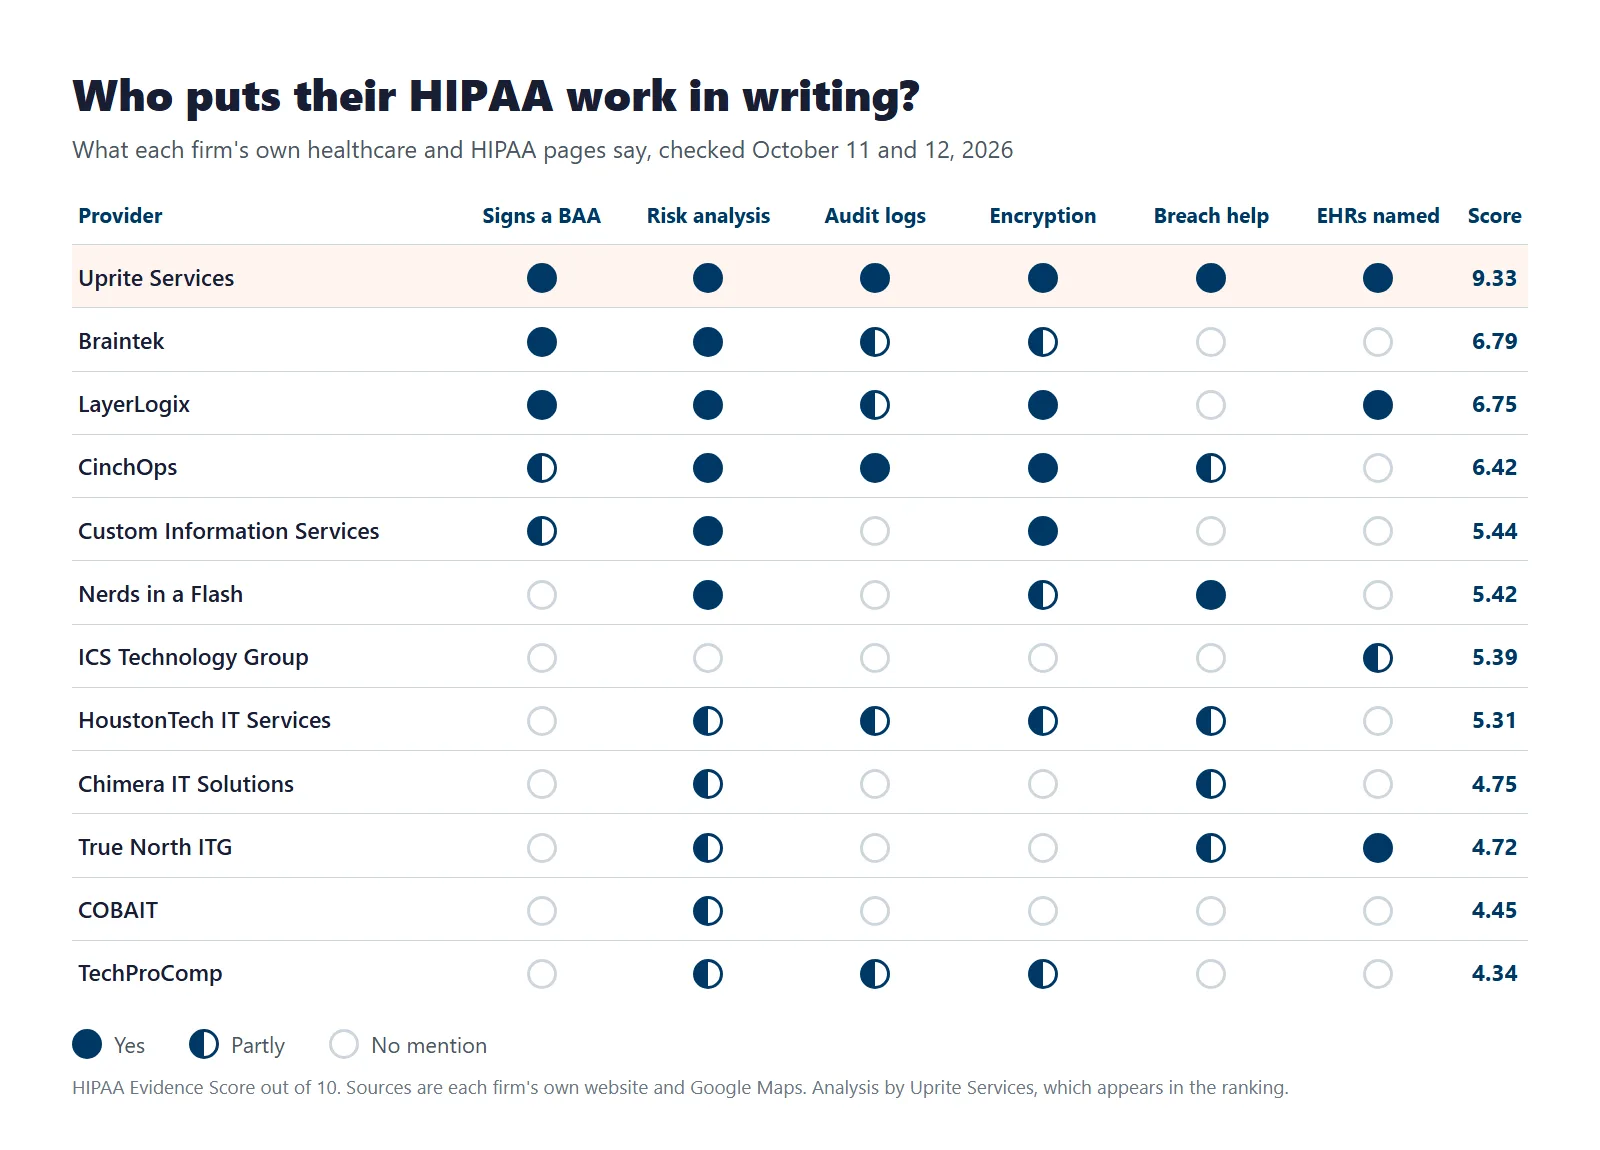
That’s the headline. Here’s the checklist behind it, the 6 things we looked for on every firm’s own healthcare and HIPAA pages.
- A signed business associate agreement. HIPAA requires the contract before a vendor handles patient data for you, and 45 CFR 164.314 says it has to make the vendor report security incidents to you, breaches included.
- A real risk analysis. Section 164.308(a)(1)(ii)(A) marks it Required and asks for an accurate and thorough assessment of the risks to your electronic patient data. A vulnerability scan isn’t one.
- Audit logs that someone reads. The audit controls standard at 164.312(b) wants systems that record activity, and a separate Required spec at 164.308(a)(1)(ii)(D) wants those records reviewed on a regular schedule.
- Encryption. Both specs are addressable. Addressable isn’t optional, though, since you either encrypt or document why it isn’t reasonable and appropriate, then use an equivalent measure if one is.
- Breach help. You have to identify, respond to, and document security incidents under 164.308(a)(6)(ii), and a business associate owes you breach notice no later than 60 calendar days after it finds one.
- EHR experience you can name. Not a HIPAA rule. We counted it anyway, because the rules exist to protect what lives inside Epic, athenahealth, or eClinicalWorks, and a firm that can’t name a single system it supports is asking you to take a lot on faith.
| Provider | Signs a BAA | Risk analysis | Audit logs | Encryption | Breach help | EHRs named |
|---|---|---|---|---|---|---|
| Uprite Services | Yes | Yes | Yes | Yes | Yes | Yes |
| Braintek | Yes | Yes | Partly | Partly | No mention | No mention |
| LayerLogix | Yes | Yes | Partly | Yes | No mention | Yes |
| CinchOps | Partly | Yes | Yes | Yes | Partly | No mention |
| Custom Information Services | Partly | Yes | No mention | Yes | No mention | No mention |
| Nerds in a Flash | No mention | Yes | No mention | Partly | Yes | No mention |
| ICS Technology Group | No mention | No mention | No mention | No mention | No mention | Partly |
| HoustonTech IT Services | No mention | Partly | Partly | Partly | Partly | No mention |
| Chimera IT Solutions | No mention | Partly | No mention | No mention | Partly | No mention |
| True North ITG | No mention | Partly | No mention | No mention | Partly | Yes |
| COBAIT | No mention | Partly | No mention | No mention | No mention | No mention |
| TechProComp | No mention | Partly | Partly | Partly | No mention | No mention |
“Partly” means the page brings the item up without saying the firm does it for you. CinchOps is a good example. It makes sure “the vendors touching your data have signed BAAs,” which is useful, but it never says it signs one itself. Close. Not the same.
Tally it up. The gaps show. 3 firms say they sign a BAA. 6 offer a HIPAA risk analysis by name. 2 describe logs being reviewed or kept, 2 describe both incident response and breach-notice help, and 3 name 3 or more EHR systems. Only 1 of the 12 names a Texas health-privacy law on the pages we read, and it’s us, even though Texas adds training and breach-notice rules on top of HIPAA that every Houston practice has to follow.
Notice what’s missing. A certificate. HHS says plainly that it doesn’t endorse or recognize private HIPAA “certifications” and that having one doesn’t stop it from finding a violation later. Our own HIPAA Seal of Compliance from Compliancy Group, earned in 2023, is exactly that kind of private badge. Good homework. Not a government stamp.
How Does the HIPAA Evidence Score Work?
The HIPAA Evidence Score gives published HIPAA safeguards 30% of the weight, Google reviews 25%, Houston presence 15%, and 4 smaller checks the last 30%, applied the same way to all 12 firms, ours included.
Rankings come from that score, 7 independently researched criteria applied identically to every provider. No provider paid for placement. Nobody sent us data. Everything below came off public pages and Google Maps on October 11 and 12, 2026.
| Criterion | Weight | What we checked |
|---|---|---|
| Published HIPAA safeguards | 30% | The 6 items above, each scored yes, partly, or no mention, from the firm’s own healthcare and HIPAA pages |
| Google reviews | 25% | Rating counts 60% and review volume counts 40% on a sliding scale, headquarters profile plus any Houston profile |
| Houston presence | 15% | A Houston-area office on Google Maps with reviews, plus stated onsite help |
| Texas health-privacy law | 10% | Whether the firm’s pages name Chapter 181 training, the Texas breach-notice statute, SB 1188 record storage, or SB 2610 |
| Years in business | 10% | The most conservative founding date the firm or a directory publishes, with named leadership |
| Own third-party audit | 5% | A SOC 2, HITRUST, or ISO 27001 report of the firm itself, with a date |
| Pricing transparency | 5% | Per-user or per-device prices anyone can read before a sales call |
Why 30% on safeguards? The title promises it. A HIPAA-compliant IT company is one that can show you the paperwork, and the paperwork is the part a practice can’t outsource its liability for. Reviews tell you whether a firm answers the phone. They don’t tell you whether it can produce a risk analysis when an investigator calls.
A few house rules. We blended each firm’s headquarters profile with any Houston profile it runs, weighted by review count, which is why our own number is 4.72 across 74 reviews instead of the 4.8 at our main office. We used Google alone, the same as our other Houston rankings, since it’s the one review source every firm here has. That costs us a little, because our Clutch profile shows 5.0 across 12 reviews. We left awards out entirely, since no major MSP list measures HIPAA work. That costs us too. We’ve been on the Channel Futures MSP 501 for 7 straight years, 264th in 2026.
Where founding dates disagreed, we took the more conservative one. That cost us most of all. Our site says we’ve served Texas since 1999, while our Clutch profile says 2008, so we scored ourselves on 2008.
The Top 5 HIPAA-Compliant IT Companies in Houston
Scores in the top 5 run from 9.33 down to 5.44. Braintek and LayerLogix sit 4 hundredths of a point apart, so treat 2nd and 3rd as a tie and pick on the item you care about most.
| Rank | Provider | Score | Nearest office | Key differentiator |
|---|---|---|---|---|
| 1 | Uprite Services | 9.33 | Westheimer Rd, Houston | The only firm of the 12 that documents all 6 HIPAA safeguards and names the Texas health-privacy rules, with per-user prices posted |
| 2 | Braintek | 6.79 | Spring | A signed BAA, a security risk assessment, and 4.9 stars across 367 Google reviews, the deepest review record here |
| 3 | LayerLogix | 6.75 | The Woodlands | Executes a BAA with every healthcare client and names 5 EHR systems, including Epic and Cerner |
| 4 | CinchOps | 6.42 | Katy | Says access to patient records is logged and reviewed, encrypts data at rest and in transit, and posts $100 to $250 per user |
| 5 | Custom Information Services | 5.44 | North Loop West, Houston | 35 years in business, with HIPAA risk assessments and encrypted email for medical and dental offices |
1. Uprite Services, the only firm that documents all 6
HIPAA Evidence Score 9.33 / 10
We’re a Houston managed IT and cybersecurity company with offices on Westheimer Road near the Galleria and on Space Center Boulevard in Clear Lake. Healthcare is one of the industries we package on its own, as Uprite MED, with managed IT services for healthcare in Houston on one side and the HIPAA program on the other.
So where did 9.33 come from? Mostly from paperwork. Boring, checkable paperwork.
- The BAA comes first. We sign one as a standard part of every healthcare engagement, and the program then confirms a signed BAA exists for every other vendor that touches your patient data.
- A risk analysis on a calendar. It runs in weeks 2 to 4 of onboarding, and then we keep the risk management plan and the evidence file current, which is the folder an investigator asks for first.
- Logs, encryption, and sign-ins. We review activity logs instead of just storing them, run full-disk encryption on every endpoint and server that holds patient data, and put phishing-resistant multi-factor sign-in on email, the EHR, and remote access.
- EHRs by name. Epic, Cerner, athenahealth, eClinicalWorks, NextGen, Allscripts, and Kareo on the medical side. Dentrix and Eaglesoft for dental.
- Prices in public. Fully managed IT in Houston starts at $138 per user per month, co-managed IT at $100, and security-only coverage at $40, all listed on our pricing page. The rate can’t rise in year 1, and you can leave within 120 days if you’re not satisfied.
People ask about speed. We average about 5 minutes to a first response. That’s an average across our clients, not a contract promise.
Now the soft spots. There are a few. Braintek and ICS Technology Group both beat us on reviews, with 4.9 across 367 and 118, and our Clear Lake office’s 4.3 pulls our blended rating down to 4.72. Reviews alone? We’d place 4th. Our only audit report is a SOC 2 Type 1 report from 2023, and we haven’t renewed it. That’s on us. And scoring ourselves on Clutch’s 2008 founding date instead of our own 1999 cost us the lead on the outside-evidence board further down.
Best for Houston clinics and groups that want one firm to run the IT and own the HIPAA evidence file, practices with 2 or more locations, and owners who want an engineer who can drive to the office. Not ideal for a health system large enough to run its own security operations center around the clock.
Services. Managed IT, co-managed IT, managed security and monitoring, HIPAA risk analysis and evidence files, backup and recovery, Microsoft 365, and vCIO planning.
Industries. Medical, dental, and specialty practices, plus construction, manufacturing, oil and gas, legal, and financial firms.
Why we rank first. Uprite Services is a Houston managed IT and cybersecurity company that runs both the IT and the HIPAA Security Rule paperwork for medical and dental practices. We rank first because we’re the only firm of the 12 that documents all 6 safeguards in writing and names the Texas rules stacked on top, not because our reviews are the best. They aren’t.
2. Braintek, the biggest review record that comes with a signed BAA
HIPAA Evidence Score 6.79 / 10
If reviews were the whole contest, Braintek would be hard to beat.
The Spring firm has done Houston IT since 2002 and carries 4.9 stars across 367 Google reviews, more than the next 3 firms on this list combined. The page is direct, too.
- “We sign business associate agreements,” and its FAQ answers the BAA question with a plain yes.
- It offers the security risk assessment HIPAA expects, scoped to an independent practice.
- $150 to $250 per device per month for fully managed support, published on the page. Rare.
Gaps hide in the details. Encryption and audit logging show up only as entries in a list of controls, with nothing on who reviews what. We found no incident response or breach-notice process described, no EHR named on either healthcare page, and no Texas statute. Beyond Google, the only credential on its healthcare page is a BBB accreditation.
Best for north Houston practices that want a long-tenured local team with a big, recent review record. Not ideal for a practice that needs its breach-response help spelled out before signing.
Why Braintek ranks 2nd. It’s the steadiest all-rounder after us, held back only by how little of its HIPAA work is described in detail.
3. LayerLogix, the longest EHR list
HIPAA Evidence Score 6.75 / 10
LayerLogix has the most specific healthcare page of any firm we scored besides our own.
It started in 2014 as My IT Guy and now runs its Houston work from Timberloch Place in The Woodlands, with 5.0 stars across 30 Google reviews. “Yes, we execute BAAs with all healthcare clients,” the page says, and it promises to “Run the Security Rule risk analysis across your whole clinic.” It names Epic, athenahealth, eClinicalWorks, NextGen, and Cerner. It turns on encryption for email, e-fax, and remote EHR access. Most Houston-area clients can get someone onsite the same day.
So why 3rd? Logs get kept but nothing says who reviews them or for how long. No breach-notice process appears. The “SOC 2 Aligned” badge in its header isn’t explained on the page, and aligned isn’t audited. No price either, since the page says it doesn’t “publish a one-size-fits-all number.” And the healthcare page’s “20+ Years Experience” badge doesn’t square with a 2014 founding, so we used 2014.
Best for practices on Epic, NextGen, or Cerner that want a firm fluent in the clinical systems. Not ideal for buyers who need a posted price before the first call.
Why LayerLogix ranks 3rd. Stronger HIPAA detail than Braintek, weaker on tenure and pricing, and those 2 things decide a 4-hundredths gap.
4. CinchOps, the clearest answer on logs and encryption
HIPAA Evidence Score 6.42 / 10
Ask most firms about audit logs and you’ll get a shrug in prose. CinchOps answers it.
The Katy firm writes that “Access to patient records is logged and reviewed,” lists log retention, encrypts patient data at rest and in transit, and says it performs “the security risk analysis the Office for Civil Rights asks for first.” It posts $100 to $250 per user per month, backs that with a 30-day guarantee, and says help desk requests get answered in under 15 minutes. 5.0 stars across 22 Google reviews.
The catch is the contract. CinchOps tracks whether your vendors have signed BAAs, but its pages never say CinchOps signs one with you. It names no EHR system and publishes no founding year, so it scored low on tenure.
Best for west Houston and Katy practices that want posted prices and specific answers on logging. Not ideal for anyone who wants years of track record before signing.
Why CinchOps ranks 4th. The best technical-safeguard detail outside our own, minus the signed BAA that would have moved it up.
5. Custom Information Services, 35 years in, with a HIPAA risk assessment
HIPAA Evidence Score 5.44 / 10
Custom Information Services, often shortened to CustomIS, has been in business 35 years and lists offices across Texas, Houston included, at a suite on North Loop West.
Its Houston HIPAA page offers HIPAA risk assessments that “identify compliance gaps and create a roadmap,” encryption and encrypted email, and vendor risk management that covers business associate agreements. It also has an online pricing calculator, which beats a blank contact form.
It slips on Houston. The only Google profile we could find is in Arlington, 4.9 across 18 reviews, so its Houston presence scored a 4. Logs, breach help, and EHR names don’t appear on the pages we read.
Best for multi-site organizations that want a long-established Texas firm. Not ideal for a practice that wants a Houston team it can verify on a map.
Why CustomIS ranks 5th. Age and a real HIPAA assessment carry it past Nerds in a Flash, by 2 hundredths of a point.
Where Do the Other 7 Scored Firms Land?
7 more firms cleared our entry gate and scored between 4.34 and 5.42, mostly because their HIPAA pages explain the rules rather than the firm’s own work.
| Rank | Provider | Score | Why it sits here |
|---|---|---|---|
| 6 | Nerds in a Flash | 5.42 | An Austin-based firm with a Richmond Avenue office in Houston and a 15-minute response guarantee. Its HIPAA page offers risk analysis and breach-reporting help, but no BAA language and no EHR names. |
| 7 | ICS Technology Group | 5.39 | 45 years in business, 4.9 across 118 Google reviews, and named clients such as Houston Eye Associates. Its healthcare pages never mention a BAA, a risk analysis, audit logs, or breach help. |
| 8 | HoustonTech IT Services | 5.31 | A southwest Houston firm whose compliance page lists risk assessment, log review, encryption, and incident response plans, all in general terms. |
| 9 | Chimera IT Solutions | 4.75 | Family-owned in Katy, with onsite coverage across greater Houston and breach-notification planning, but little else described. The old OverBytes web address now forwards here. |
| 10 | True North ITG | 4.72 | Healthcare-focused, with Epic, NextGen, and athenahealth on its Houston page. Its only Google profile, though, is in Mill Creek, Washington. |
| 11 | COBAIT | 4.45 | Gives its managed healthcare clients a “HIPAA Aware Seal” after yearly audits, yet its HIPAA page says little about the firm’s own safeguards. |
| 12 | TechProComp | 4.34 | An Austin-headquartered firm with a Houston office listed on its site, a managed SIEM service, and a 3-hour guaranteed response on critical issues. |
Places 5, 6, and 7 sit within 5 hundredths of each other. Call it a dead heat.
What If You Ignore What Each Firm Says About Itself?
Count only what a stranger can check without trusting anyone’s marketing, meaning Google reviews, a Maps-verified office, a third-party audit, and years in business, and ICS Technology Group edges us out, 8.98 to 8.78.
Why run it? Three of our 7 criteria, the safeguards, the Texas law, and the prices, come off each firm’s own website. Anyone can type “we sign BAAs.” So we built a second board that drops all three and reweights the rest.
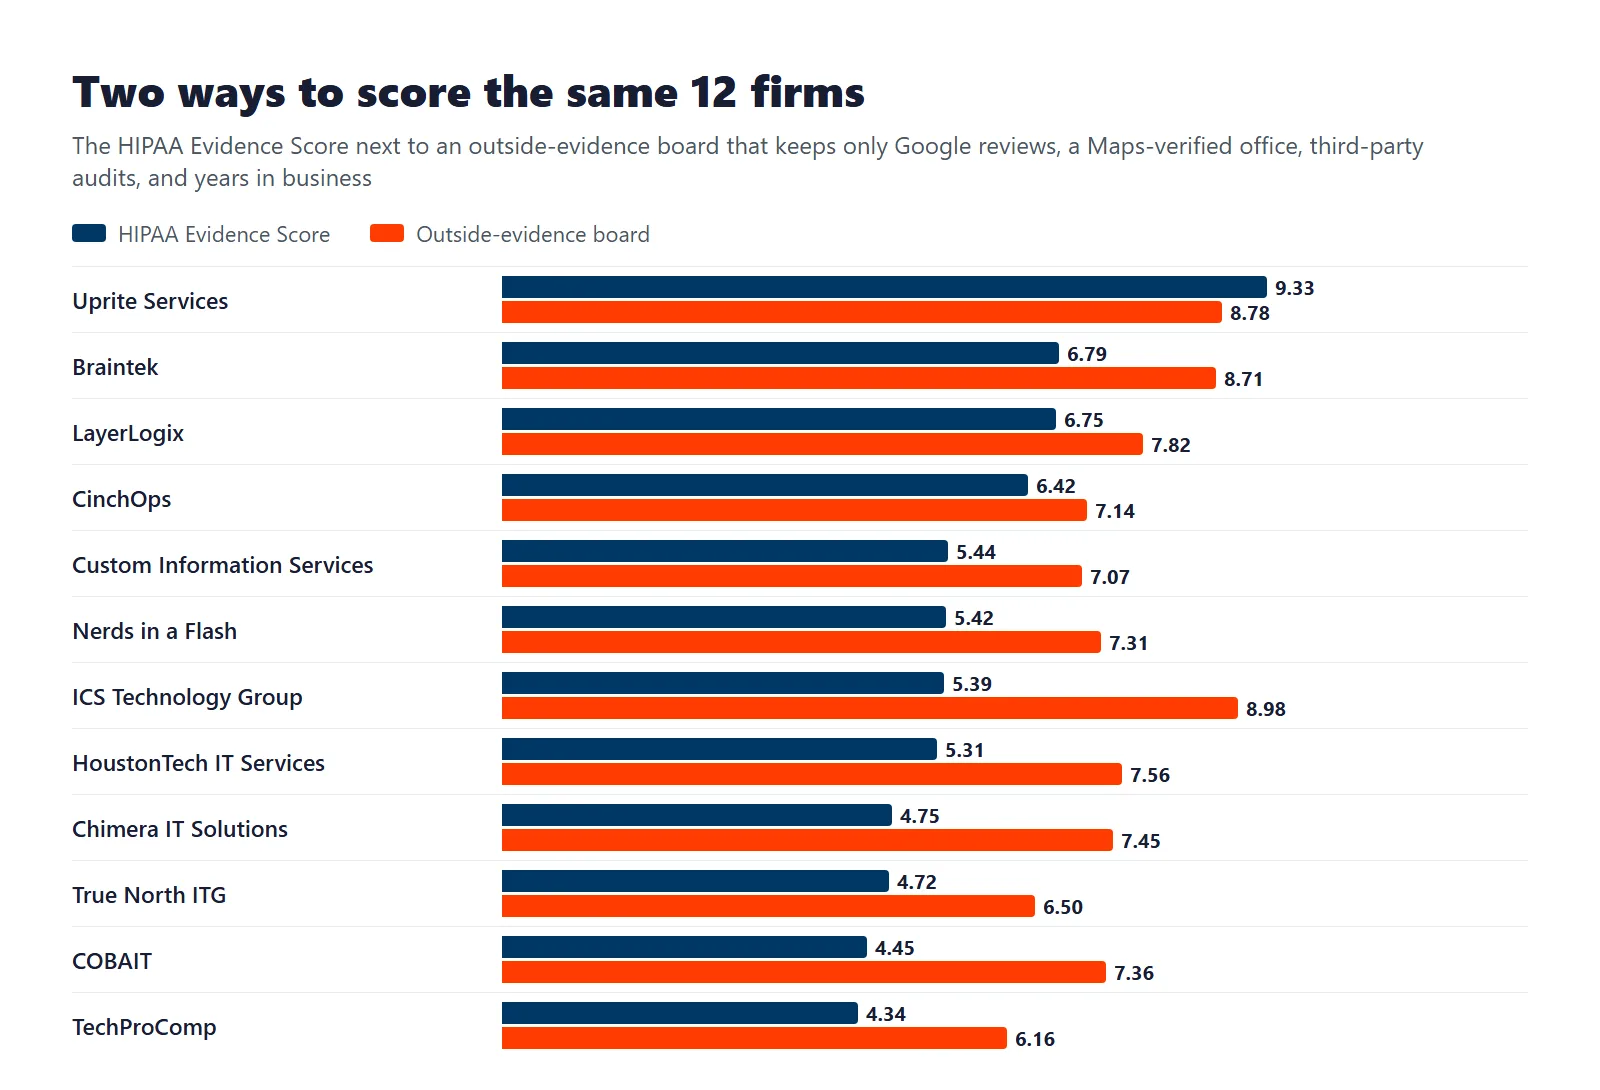
ICS wins it on 45 years in business and 118 strong reviews. Fair enough. We land 2nd, and Braintek is a breath behind at 8.71. LayerLogix follows at 7.82, then HoustonTech at 7.56. And if we’d scored ourselves on our own 1999 founding date instead of Clutch’s 2008, we’d have taken this board back, 9.15 to 8.98. We didn’t, for the same reason nobody else got to pick their best number.
Our read? A firm with great reviews and no HIPAA paperwork is a good help desk. Not a HIPAA program. Ask any firm here, ICS and us included, to send a draft BAA and a redacted risk analysis before you sign, and see who answers with documents.
Which Firms Didn’t Make the Cut?
6 names we checked never got a score of their own. OverBytes IT Solutions, our February number 3, now forwards to Chimera, which we scored under its current name. Werner Technology Solutions, number 4 in our February edition, lists financial firms, law firms, manufacturing, energy, and engineering on its site, but no healthcare. Centre Technologies has a Greenspoint office, 4.8 across 65 Google reviews, and an MSP 501 badge, yet we found no healthcare or HIPAA service page, only a blog post. Cloud Cat Services lists offices in Nashua, New Hampshire, and Boston, and its Houston page still carries a “Cambridge IT Support” FAQ heading. Stratify IT writes some of the sharpest HIPAA copy we read, Texas statutes and all, from New York. Layer One Networks is a Corpus Christi firm whose site has no healthcare or HIPAA page. And TopCertifier and Medcurity, both named in Google’s AI answers, sell HIPAA consulting or software rather than managed IT.
What Do Houston Breach Notices Say About Picking a Vendor?
In the 12 months to October 6, 2026, the Texas attorney general posted 138 breach notices from healthcare providers, and 18 came from Houston-area practices, clinics, hospitals, and labs.
Those 18 covered 629,611 Texans, per the attorney general’s data security breach list, which we pulled in full on October 11. Two notices, from a Conroe health center and a Houston genetics lab, make up 79% of that. Lopsided. The typical one was small. Half involved fewer than about 3,650 Texans, and medical information showed up in 119 of the 138 healthcare notices statewide.
The part that matters for picking a vendor is the small end. 6 of the 18 Houston notices involved fewer than 500 people in total, the line below which the federal breach portal says cases “may be investigated based on Departmental resources and enforcement priorities.” Texas listed every one of them anyway. Its law sends any breach touching 250 or more Texans to the attorney general within 30 days, on top of the 60 days you get to tell patients.
Now the clause nobody reads. Under the Texas breach-notice statute, a company that maintains data it doesn’t own, which describes your IT company, has to tell the owner “immediately after discovering the breach.” HIPAA lets a business associate take up to 60 days. Which clock does your contract use? Ask. Every week a vendor sits on a breach is a week your practice can’t spend investigating, telling patients, or filing with the state.
How Do You Choose a HIPAA-Compliant IT Company in Houston?
Ask for paper before price. A Houston IT company that will send a draft BAA, a redacted risk analysis, and its log and encryption settings before you sign belongs on your shortlist, and one that won’t is a help desk with a HIPAA page.
Then match the fit.
- A small clinic with no IT person. You need the BAA, a risk analysis, and backups someone actually tests. Three firms here post prices (us, CinchOps, and Braintek), so you can budget before anyone calls you back.
- Two or more locations. Onsite reach starts to matter, because the second office always breaks on the day the first one is busy. Look for a Maps-verified Houston office and a stated onsite promise.
- You already have IT staff. Buy the compliance layer, not a replacement. Our co-managed plan starts at $100 per user per month and leaves your people in charge of the systems they run.
- A practice on Epic, NextGen, or Cerner. LayerLogix and True North ITG name the most EHR systems after us.
- A dental office. Different software, different checklist. Our ranking of the best IT providers for dental practices in Houston scores dental depth instead.
Ask one trick question, too. How often does Texas law say your staff must be trained? The current answer, from Health and Safety Code 181.101, is within 90 days of hire and within a year of any material change in privacy law, with a signed statement kept for 6 years. If a vendor quotes a 2-year cycle, that rule was struck by SB 1609 in 2013. Their material is 13 years stale.
For the technical side, NIST SP 800-66 Revision 2 from February 2024 walks through the Security Rule standard by standard, and the joint event logging guidance CISA co-signed in August 2024 covers what to log and why. Neither is light reading. Both beat a brochure.
And if you already have a compliance officer, a risk analysis dated in the last year, and an IT team that reads its own logs, you may not need any firm on this list. Truly. If day-to-day clinical support matters more to you than paperwork, our ranking of healthcare IT support providers in Houston scores that instead, and our list of healthcare cybersecurity firms in Houston covers security-only buyers. Budgeting the whole program? Here’s what a HIPAA compliance program costs a Texas practice.
Want your HIPAA paperwork checked before you switch?
Book a free HIPAA gap review. We’ll read your current BAA, your last risk analysis, and your backup settings, then tell you what an investigator would ask for first and whether your current IT company can answer it.
Speak to an IT ExpertOr check our published prices
What Houston Practices Ask Before Signing With a HIPAA IT Company
Can an IT company be HIPAA certified?
Not by the government. HHS says it doesn’t endorse or recognize private HIPAA “certifications,” and that one doesn’t stop it from finding a violation later. What counts is a signed BAA and the safeguards behind it. Badges, ours included, are homework.
What should our BAA with an IT company say about breaches?
Two deadlines, in writing. HIPAA requires the agreement to make the vendor report security incidents and breaches, with breach notice due no later than 60 calendar days after discovery, while Texas law tells a company holding data it doesn’t own to notify the owner immediately.
Ask for the faster one. Every week a vendor waits is a week you can’t use.
Does Texas still require HIPAA training on a 2-year cycle?
SB 1609 removed that in 2013. Texas now requires training within 90 days of hire and within a year of a material change in privacy law, plus a signed statement kept for 6 years. The old rule still turns up in older checklists, a few of ours included until this September.
What should an IT company show us before we sign?
Five documents, and none of them is a sales deck. A draft BAA, a redacted sample risk analysis, its log review and retention routine, a list of what it encrypts, and an incident response plan with real names in it.
A firm that can’t produce those within a week is guessing.
Why does a ranking published by Uprite put Uprite first?
Fair question. We wrote it, so we scored ourselves with the same rules as everyone else and then published a second board that drops everything firms say about themselves. On that board ICS Technology Group beats us. Judge the method.
Which of these firms fits a small Houston clinic?
Start with the 3 that post prices. Our fully managed plan starts at $138 per user per month, CinchOps quotes $100 to $250 per user, and Braintek $150 to $250 per device. Then ask each one for the BAA before anything else.
What if our current IT company won’t sign a BAA?
Then it shouldn’t be handling your patient data. HIPAA requires a written agreement before a vendor creates, receives, maintains, or transmits protected health information for you, and a firm that refuses is telling you how it would behave after a breach.