A cybersecurity risk assessment in Houston costs roughly $3,000 to $25,000 from an outside firm, and what you get back is a written, ranked list of what could hurt the business and what to fix first. It’s also where our vCISO services in Houston begin, because a security program written without one is a guess.
We went looking for a price first and didn’t find one. Houston provider pages we read either say to request a quote or give the first review away. Not one printed a figure for a standalone assessment. So we built the number ourselves from hours and public labor rates, and every input is on the page so you can check it. A proposal on your desk gets the same test. Ours too. Uprite does its own assessment free, as part of our cybersecurity services in Houston, with no obligation to hire us afterward. A section near the end covers where that review stops.
6 documents come out of a finished assessment. An asset and data inventory. A threat and weakness list. A control gap map, a risk register, a ranked fix list, and a short executive summary. Outside firms put 20 to 120 hours into that, which at public labor rates is about $2,800 to $25,400 depending on headcount and sites. Free scanners handle the technical part. HIPAA and the FTC rule still want the written ranking.
What do you get from a cybersecurity risk assessment?
A cybersecurity risk assessment is a documented review of what a company holds and runs, what could realistically go wrong with each piece, and how likely and how costly each problem is. What comes out is a ranked list with an owner and a fix beside every item, and the scan output goes in an appendix.
NIST supplies the outline. Special Publication 800-30, the federal guide to conducting risk assessments, uses 4 steps. Prepare, conduct, communicate, maintain. The Cybersecurity Framework 2.0 files the same work under Identify, in a category called Risk Assessment. It starts at ID.RA-01, which is recording the vulnerabilities in your assets. It ends at ID.RA-10, which is checking critical suppliers before you buy from them.
| Deliverable | What’s in it | The question it answers |
|---|---|---|
| Asset and data inventory | Systems, cloud accounts, vendors, and every place regulated data lives | What do we actually have to protect? |
| Threat and weakness list | Realistic ways each asset could be hit, and the gaps that would let it happen | What could go wrong here? |
| Control gap map | Current safeguards scored against a framework such as NIST CSF 2.0 or CIS Controls IG1 | Where do we fall short of the standard? |
| Risk register | Each risk rated for likelihood and impact, with a named owner | Which problems matter most? |
| Ranked fix list | Remediation steps in priority order, with effort and rough cost | What do we do first, and what will it cost? |
| Executive summary | A short readout for ownership, an insurer, or a customer’s security team | What do we tell the board or the auditor? |
Ask for a sample risk register and fix list before you sign. A register that rates everything high, medium, or low with no owner and no date is a draft, whatever the cover says. The fix list is the part that earns the fee. It’s what your IT team can open on Monday morning and start working through.
How is a risk assessment different from a vulnerability scan or a penetration test?
People mix these 3 up all the time, and a few quotes blur them on purpose. A scan lists known weaknesses. A penetration test tries to use them. An assessment decides which ones would hurt you most, and it takes the first two as inputs. The first two are compared in our Houston guide to scans and pen tests.
| Service | The question it answers | What you get | Who does the work |
|---|---|---|---|
| Vulnerability scan | Which known weaknesses are on my systems right now? | A findings list sorted by severity | Software, run on a schedule |
| Penetration test | Can someone actually get in? | Proof of an attack path, plus fixes | A human tester, quoted by scope |
| Risk assessment | What matters most to this business, and what do we fix first? | A ranked register and a roadmap | A security professional who interviews your team |
Want to know if someone can break in? That’s a test, and we’ve covered penetration testing in Houston and what a penetration test costs in Houston. But a company that has never done either should start here. A tester handed no inventory spends half the engagement chasing a file server nobody remembered owning.
What happens during a Houston risk assessment, step by step?
The Department of Health and Human Services doesn’t dictate a method. Its guidance on risk analysis does list what any method must cover, and that list fits a bakery as well as a hospital. In practice the work runs in 6 steps.
- Scope first, meaning the sites, systems, cloud tenants, and rules in play, plus who will answer questions.
- Then data collection, from interviews, existing documents, and exports out of tools you already pay for.
- A written list of threats and weaknesses for each asset.
- A look at which safeguards exist and whether anyone configured them correctly.
- A likelihood rating and an impact rating for every threat, which together set the risk level.
- A walkthrough with leadership for the register and fix list, and a date for the next review.
The process doesn’t end when the report does. HHS names events that call for a fresh look, among them a security incident, a change in ownership, turnover in key staff, and new technology. Houston has its own. After a hurricane scatters your staff and systems for a few weeks, last year’s inventory describes an office that no longer exists. Planning figure for a 50-person company, 2 to 4 weeks on the calendar, mostly waiting on interviews and exports. That’s our estimate and no standard backs it.
What does the Texas breach list show a Houston company holds?
Texas wants a notice sent to the Attorney General whenever a breach touches 250 or more Texans, and the office posts them in its data security breach report. We counted entries posted between October 30, 2025 and October 28, 2026 for organizations in Houston and nearby cities. There were 76. Social Security numbers appeared in 65. Driver’s license numbers, 45. Financial account details, 36. Medical information, 35. Health insurance data, 34.
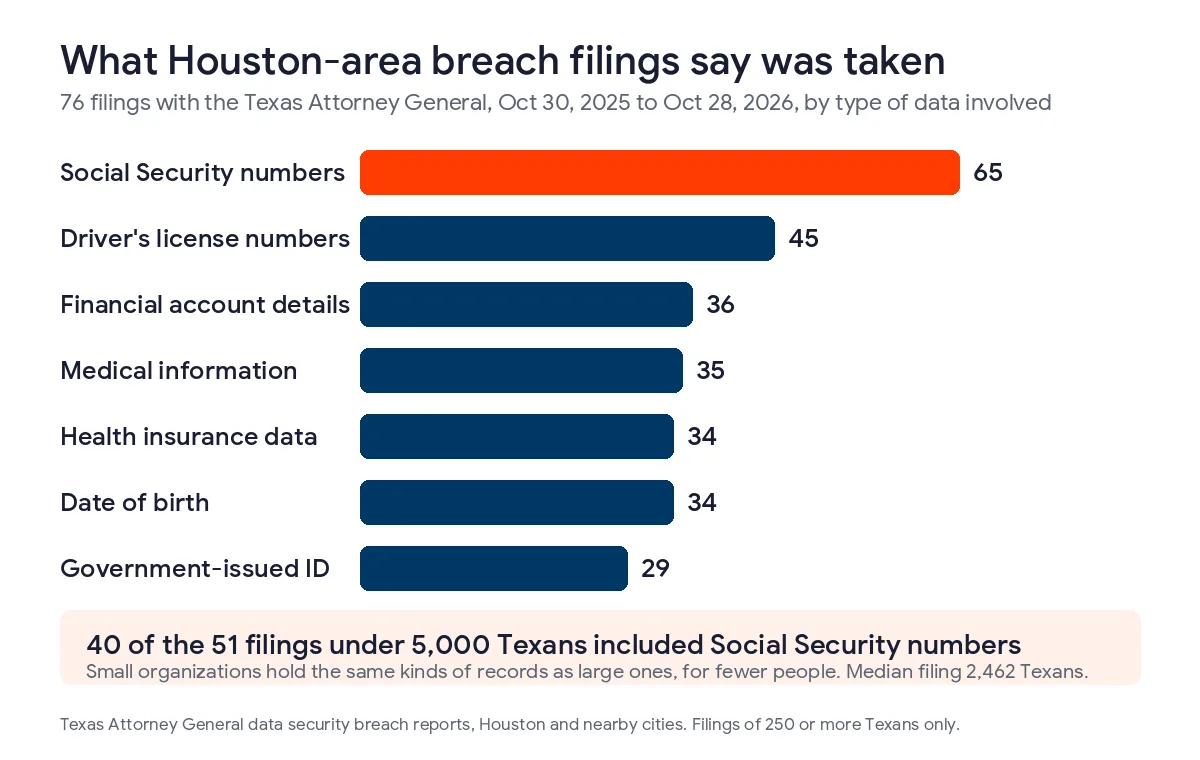
The size surprised us. Median filing, 2,462 Texans. Fifty-one of the 76 involved fewer than 5,000 people, and 40 of those 51 included Social Security numbers. Nineteen filers were healthcare providers, 10 were financial or insurance firms (CPA practices among them), and 7 were nonprofits or schools. Another 40 filed as retail, merchant, or other, which in Houston means energy services, industrial suppliers, and construction firms.
So what does that change? A small Houston company holds the same kinds of records a big one does, just about fewer people. That’s why the inventory comes first. You can’t rank the risk to a Social Security number nobody knew was sitting in a shared drive. One caution. The list skips breaches under 250 Texans and counts filings, not companies, so it understates the problem.
How much does a cybersecurity risk assessment cost in Houston?
Cost is hours times a rate. Our table prices 3 planning bands, and the hours are our own estimates. Its first dollar column is a labor floor, what an hour of an information security analyst’s time costs an employer in Houston. The second is a market range built from public rates for outside risk assessment specialists.
| Company profile | Planning hours | Labor floor (BLS) | Market range (GSA, middle half) |
|---|---|---|---|
| Under 25 employees, 1 office | 20 to 30 | $1,750 to $2,620 | $2,810 to $6,360 |
| 25 to 99 employees, 1 or 2 sites | 40 to 60 | $3,490 to $5,230 | $5,620 to $12,720 |
| 100 to 249 employees, several sites or regulated data | 80 to 120 | $6,980 to $10,470 | $11,230 to $25,450 |
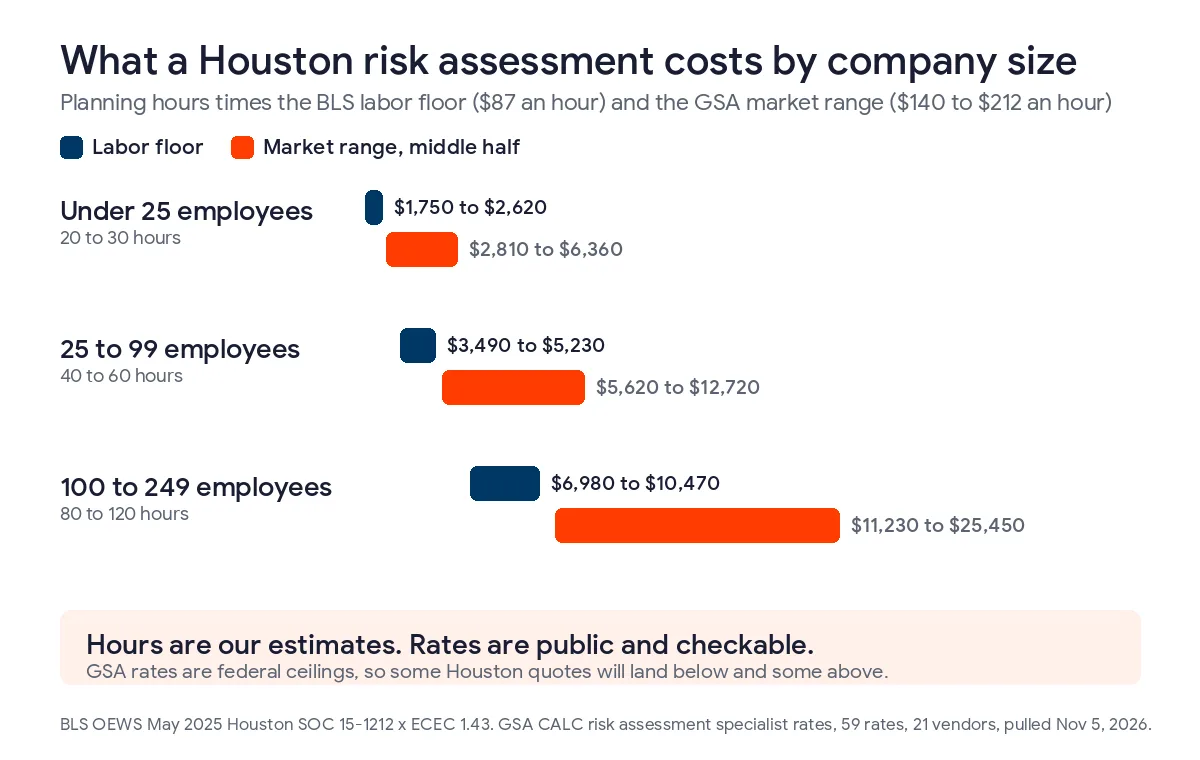
Start with the floor. BLS’s May 2025 Occupational Employment and Wage Statistics count 2,110 information security analysts in the Houston area, earning a mean of $61.00 an hour. In June 2026 private employers paid $46.89 in total compensation for every $32.82 of wages, per BLS’s Employer Costs for Employee Compensation. That’s a ratio of 1.43. Multiply, and an analyst hour costs about $87 with benefits in.
The market range comes from GSA’s federal labor rate data, which we pulled on November 5, 2026. Risk assessment specialist titles with no clearance requirement gave us 59 rates from 21 vendors. Median, $174.30 an hour. Middle half, $140.38 to $212.07. Titles asking for 8 or more years of experience have a median of $206.68, against $130.77 for 3 years or less.
These are ceilings. They’re the most a vendor may charge a federal agency, so they aren’t a commercial price list, and plenty of Houston firms will quote under them while a few boutique shops quote over. A quote below the labor floor should make you ask who’s actually doing the work. Firms still have to cover a backup person, tools, and insurance.
What makes one assessment cost more than another?
Hours drive the price, and 6 things add them. Headcount, because every account and laptop gets inventoried. Sites and cloud tenants, which jump when an acquisition leaves you holding a second Microsoft 365 tenant. Regulated data, whether it’s HIPAA, the FTC rule, or a customer contract. Scanning, which can double the technical hours when it’s bundled and shows up as its own line when it isn’t. Policies and an asset list already on file, which shorten the interviews. And a signature requirement, since a report signed for a regulator, an insurer, or a customer takes longer than an internal one.
Year one costs more than year two. Once the inventory exists, a refresh is mostly checking what changed. A provider quoting the same hours every year should be asked why.
Which rules expect a written risk assessment?
Three rules come up often in Houston. In each, the assessment is where the rest of the compliance work starts. Uprite isn’t a law firm, so have counsel confirm how they apply to you.
HIPAA
Medical practices, dentists, and the vendors that handle their patient data answer to 45 CFR 164.308, which calls for an accurate and thorough assessment of the risks to electronic protected health information. HHS leaves the format to you. It doesn’t leave the documentation to you, and investigators typically ask for the analysis early after a breach. Our HIPAA cybersecurity guide for Houston covers the rest of the Security Rule.
The FTC Safeguards Rule
Tax preparers, CPA firms, mortgage brokers, and car dealers that arrange financing fall under 16 CFR 314.4. It builds the whole security program on a written risk assessment, with criteria for rating each risk and a plan for how safeguards address it. Section 314.6 gives a break to firms holding customer information on fewer than 5,000 consumers, and the written assessment drops out. Count your records before you shop.
Texas SB 2610
Texas SB 2610 has been in force since September 1, 2025, and it ties protection from exemplary damages to headcount. At 100 to 249 employees you need a security program that conforms to a recognized framework, and the assessment is where you document where you conform, where you don’t, and when you checked. Smaller companies need lighter measures, laid out tier by tier in our SB 2610 compliance guide.
Can free tools replace a paid assessment?
Partly. CISA’s Cyber Hygiene services cost nothing for public and private critical infrastructure organizations. The vulnerability scan watches your public, static IPv4 addresses and sends weekly reports. Web application scans report monthly. CISA says service typically starts within 3 business days of sign-up. Small healthcare practices also get the HHS and ONC Security Risk Assessment Tool, which walks through the HIPAA questions in order.
What none of these tools do is weigh a finding against your business. A scan can flag an exposed server without knowing it holds payroll files for 400 people, each owed a breach notice if it fell over. Under 20 employees and no regulated data? Free tools plus our guide to conducting a cybersecurity risk assessment yourself and the cybersecurity checklist for Houston small businesses may be enough. Past that size, the ranking is worth paying for.
How does Uprite run a cybersecurity risk assessment in Houston?
Ours is free, and you can walk away afterward. We map your environment, find what’s exposed, and hand you a prioritized picture of the risks.
It isn’t the signed document some regulators and insurers ask for. The formal written version, with each risk named and dated, is one of the working parts of our vCISO engagements, which we price by scope. Our guide to vCISO cost in Houston shows how to check a quote with hourly math, and the best vCISO providers in Houston ranking helps you compare offers. Monitoring and tools after an assessment fall under managed security services in Houston, with the stack priced in cybersecurity cost in Houston.
What should a risk assessment quote spell out?
When you compare proposals, check that each one covers these 7 items.
- The standard it follows, whether NIST CSF 2.0, CIS Controls IG1, or the HHS elements.
- How many hours, who does the work, and who covers when that person is out.
- Whether technical scanning is inside the price or a separate line.
- Which deliverables arrive, with a sample risk register and fix list attached.
- Whether the report is signed, and by whom.
- Who keeps the report and its evidence if you leave.
- The date of the next review, and its price.
Item 6 is the one buyers skip. Months from now a customer, an insurer, or a court may ask what you knew and when, and a dated assessment answers it. If the only copy lives in a provider’s portal, it can vanish when the contract ends.
Risk assessment questions Houston companies ask
How much does a cybersecurity risk assessment cost for a 50-person Houston company?
Roughly $5,600 to $12,700. That’s 40 to 60 hours at the middle half of public rates for risk assessment specialists, $140 to $212 an hour. Hold any quote against that, and against ours, which is free.
How long does a risk assessment take?
Two to 4 weeks on the calendar for about 50 people. Hands-on work runs 40 to 60 hours. Most of the waiting is interviews and exports from your cloud and security tools.
How often should we repeat it?
At least once a year, and again after any big change. HHS lists a security incident, a change in ownership, turnover in key staff, and new technology as triggers. Year two usually costs less because the inventory already exists.
Is a risk assessment the same as a penetration test?
No. A penetration test tries to break into specific systems and shows what an attacker could reach. A risk assessment ranks every threat to the business and takes any test result as one input. Start with the assessment if you’ve done neither.
Do we need a written risk assessment for HIPAA or the FTC Safeguards Rule?
Yes, if the rule covers you. HIPAA requires an accurate and thorough risk analysis under 45 CFR 164.308. The FTC rule requires a written risk assessment under 16 CFR 314.4, unless you hold information on fewer than 5,000 consumers.
Can we do a risk assessment ourselves with free tools?
Partly. CISA’s free scanning and the HHS Security Risk Assessment Tool find exposures and walk you through questions. They can’t rate business impact. Companies with regulated data, or more than about 20 employees, usually bring someone in.
Tell us your headcount, your sites, and the rules you answer to. We’ll run a free cybersecurity risk assessment for your Houston company and send back a ranked list of what to fix first, whether you hire us or not.
Request a free risk assessment