Fully managed IT fits a Texas business with no internal IT staff or no appetite to own IT, while co-managed IT fits a company whose internal IT lead can hold the keys and hand specific duties to a provider. That’s the textbook answer. It’s right, as far as it goes. It just doesn’t go far enough for a company that operates under Texas law. Before you compare quotes for co-managed IT services or a fully managed plan, answer 3 questions most comparisons skip. Who holds the admin keys? Who signs the security evidence? Who files the breach notice?
Short version. Headcount alone won’t pick your model. Ownership will. Under fully managed IT the provider holds the admin credentials and runs the security program. Under co-managed IT a named person on your payroll owns the environment, and the provider operates a written slice of it. Texas raises the stakes, because SB 2610 ties its safe harbor to a documented program sized to your headcount, and a breach touching 250 or more Texans starts a 30-day clock with the Attorney General.
I run Uprite, and we sell both models. Our fully managed plans run $91 to $138 per user per month. Our co-managed partnership starts at $100. So I don’t have much reason to push you toward either one. I do have a reason to push you away from the wrong one. A mismatched model costs more to unwind than either model costs to run.
If you want the general side by side first, with definitions, pricing and a switching plan, our broader comparison of the 2 models covers it well. This post is narrower. It’s about ownership. And it’s about 3 Texas facts that change who should own what.
What Is the Real Difference Between Co-Managed and Fully Managed IT?
Fully managed IT is an arrangement where an outside provider runs your entire IT function and holds the administrative authority to do it. Co-managed IT is an arrangement where an internal IT owner keeps that authority and contracts a provider to operate defined parts of the environment, such as monitoring, security or after-hours support.
Both definitions hide the same word. Authority. Whoever holds the global admin account in Microsoft 365, the firewall login and the backup console is the one actually running your IT, whatever the contract happens to call the arrangement.
That’s why I don’t treat co-managed as the budget version of fully managed. It isn’t. Per user, it often costs about the same, because the provider still brings the tooling, the monitoring stack and the after-hours bench. What you save is scope. Not rate.
Our breakdown of co-managed IT pricing in Texas shows the per-user and per-ticket math in full, including why a $40 security-only tier exists for teams that need nothing but the security layer from an outside partner.
Why Isn’t Having IT Staff Enough to Decide?
Nearly every comparison starts with that question. Do you employ IT people? If not, go fully managed. If so, go co-managed. It’s a good first filter. It’s a bad final answer.
Here’s the problem. Having an IT person isn’t the same as having an IT owner. Ownership takes 3 things. The authority to make changes. The skills to judge a provider’s work. The time to check it. Plenty of Texas companies give an IT employee the first of those and never provide the other 2, which is how a capable technician ends up holding authority that nobody is checking.
The skills side keeps getting harder. The 2025 ISC2 Cybersecurity Workforce Study, which surveyed 16,029 security professionals, found that 95% of respondents reported at least 1 skill need and 59% cited critical or significant ones, a 15 point jump from 2024.
Salaries don’t make it easier. The Bureau of Labor Statistics puts the median wage for network and computer systems administrators at $99,130 as of May 2025, and it projects employment in that occupation to fall 4% over the next decade. So you’d be paying close to 6 figures for a generalist, while the security specialists those ISC2 respondents can’t find stay out of reach.
NIST wrote the underlying idea into its Cybersecurity Framework 2.0. It asks organizations to make sure cybersecurity roles, responsibilities and authorities are established, communicated, understood and enforced. Look at the last word. Enforced. A co-managed contract that nobody on your side can enforce is really a fully managed contract with extra meetings.
Who Holds the Keys Under Each Model?
This is the table I’d want in front of me before signing either agreement. Each row is a duty someone must own by name. The columns show where that duty usually lands. Read it slowly.
| Duty | Fully managed IT | Co-managed IT |
|---|---|---|
| Global admin accounts (Microsoft 365, firewall, backups) | Provider holds them, and your company keeps a sealed break-glass copy | Your IT lead holds them, and the provider gets scoped, MFA-protected access |
| Security tooling (EDR, email filtering, log monitoring) | Provider selects, runs and licenses it | Usually provider-run, sometimes your existing stack |
| Patch approval and change windows | Provider decides within the agreement | Your IT lead approves, and the provider executes |
| Backup restore testing | Provider tests and reports | Split, and the split must be written down |
| Declaring a security incident | Provider detects, and your executive decides | Either side detects, and your IT lead declares |
| Filing the Texas Attorney General breach notice | Your company, always | Your company, always |
| SB 2610 program documentation | Provider maintains it, and you adopt it | Your IT lead owns it, and the provider supplies evidence |
| Cyber insurance application answers | Your executive signs, and the provider supplies the facts | Your executive signs, and your IT lead verifies the facts |
| On-site hands during an outage | Provider dispatches | Your IT lead first, provider as backup |
| Roadmap and budget | Provider’s vCIO proposes, and you approve | Your IT lead proposes, and the provider advises |
Two rows never move. Your company files the breach notice. Your executive signs the insurance application. No contract transfers either one, which tends to surprise owners who picked fully managed because they wanted IT off their plate entirely.
Federal guidance says the same thing from the other direction. The joint CISA advisory on cyber threats to managed service providers and their customers tells customers to make sure they have a thorough understanding of the security services their provider delivers under the contract. It says contracts should detail how and when the provider notifies the customer of an incident. It also calls for MFA on every provider account that touches a customer environment, treated as privileged. Put all 3 in writing. Whichever model you pick.
None of this is theoretical. Verizon’s 2025 Data Breach Investigations Report found that the share of breaches involving a third party doubled to 30%. Your provider is a third party. So is its software.
Which Model Fits Your SB 2610 Size Tier?
Texas gave smaller companies a concrete reason to formalize all of this. Senate Bill 2610, in effect since September 1, 2025, bars a person harmed by a breach from recovering exemplary damages from a business with fewer than 250 employees, as long as that business maintained a qualifying cybersecurity program when the breach happened. The bill scales the program to headcount.
That scaling lines up well with the model decision.
| Employees | What SB 2610 asks for | Model that usually fits |
|---|---|---|
| Fewer than 20 | Simplified requirements, including password policies and employee cybersecurity training | Fully managed, because a firm this size rarely has an IT owner to share the work with |
| 20 to 99 | Moderate requirements, including CIS Controls Implementation Group 1 | Either one, decided by whether your IT person can own 56 safeguards and their evidence |
| 100 to 249 | An industry-recognized framework, such as the NIST Cybersecurity Framework or ISO/IEC 27001 | Often co-managed, because companies this size tend to employ an IT manager who can own a full framework |
| 250 or more | Outside the safe harbor entirely | Either one, and the evidence burden rises regardless |
The middle tier is where most of the real decisions happen. CIS Controls Implementation Group 1 contains 56 safeguards, and CIS describes it as essential cyber hygiene. Asset inventory. Secure configuration. Account management. Data recovery. Each one needs a named owner and a dated record showing it’s being done, and that record has to exist before a breach, because nobody believes documentation written the week after an incident.
So ask your internal IT person a blunt question. Could you produce evidence for all 56 by Friday? If the honest answer is yes, with some help, co-managed fits. If the honest answer is a long pause, you’re describing a fully managed engagement, whatever name ends up on the contract.
One caution. The statute doesn’t certify anyone, and it doesn’t require you to hire a provider at all, so a company with a disciplined internal team can qualify on its own, and a company with a provider can still fall short if nobody keeps the records. It shields you from exemplary damages. It doesn’t stop the breach or the ordinary damages that follow. Our SB 2610 compliance guide walks through each tier in more depth, and your attorney should confirm how your program would hold up.
Who Runs the 30-Day Texas Breach Clock?
Texas shortened its notice window in 2023. Under Section 521.053 of the Business and Commerce Code, a business must notify the Attorney General as soon as practicable and no later than the 30th day after it determines a breach occurred, whenever the breach involves at least 250 Texas residents. Affected individuals get 60 days.
30 days sounds generous. It isn’t. In practice the first week disappears into scoping, forensics, calls with your insurance carrier and working out whose records were touched, and you can’t even count the affected Texans until that work is done. And somebody has to make the determination call that starts the clock. Who that person is depends on your model.
Under fully managed IT, the provider usually sees the alert first and escalates to an executive who has never run an incident, which puts the first big decision on the person least practiced at making it. Under co-managed IT, your IT lead sees it alongside the provider and can make the call, provided the contract says so and provided that person isn’t on a plane, on vacation or asleep when the provider’s analyst picks up the phone. Both work. What fails is the version where each side quietly assumes the other one is declaring, so the alert sits in a queue while the 30-day window keeps running and nobody writes anything down.
Getting it wrong keeps getting pricier. IBM’s Cost of a Data Breach report now puts the global average breach at $4.99 million, a record high and 12% above the prior year. For smaller firms the dominant threat is ransomware, which the same Verizon report found in 88% of breaches at small and midsize organizations.
Write the declaration rule into the agreement. 1 sentence is enough. Something like this works. The internal IT manager declares incidents, and the provider notifies that person within 1 hour of detection.
What Happens When the Power Goes Out in Houston?
Texas adds a problem most national comparisons ignore. Weather takes out whole metros at once.
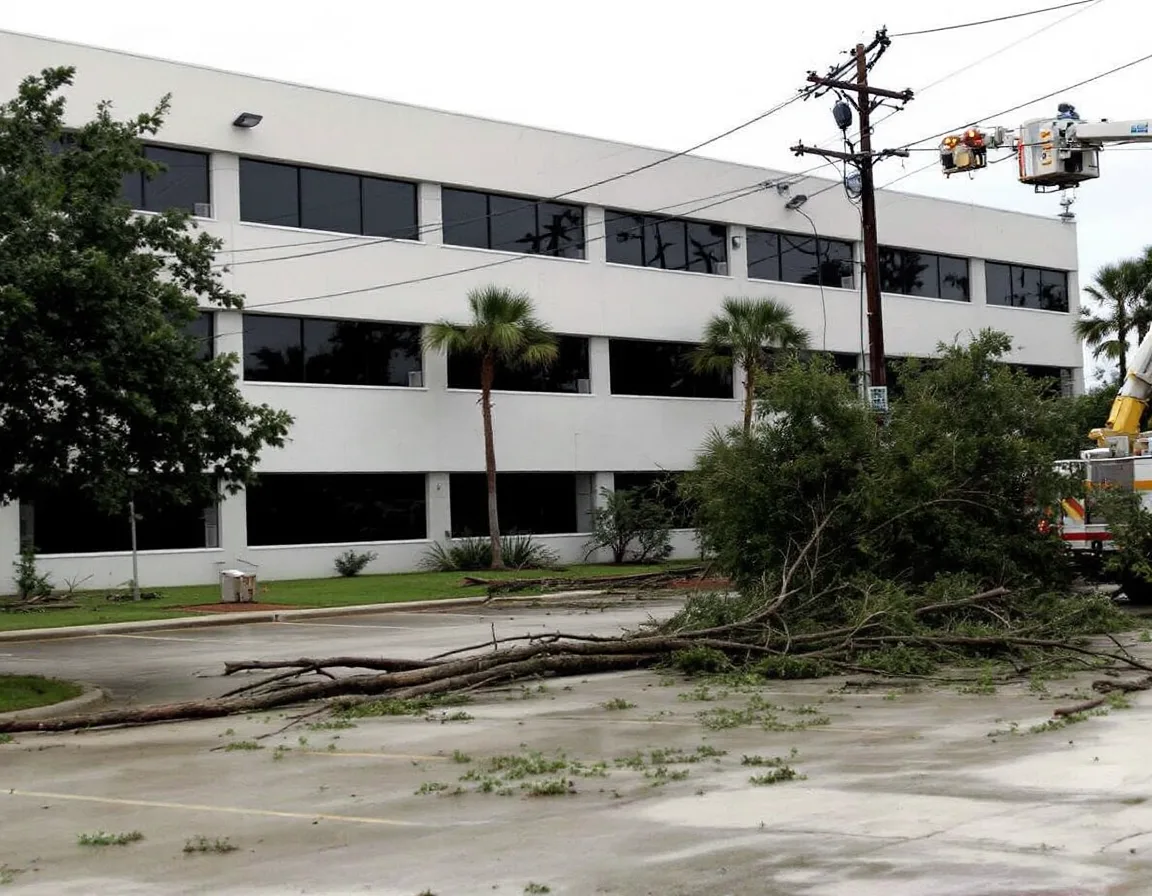
When Hurricane Beryl made landfall on July 8, 2024, some 2.26 million CenterPoint customers lost power, and hundreds of thousands still had none a week later, the Texas Tribune reported. That was an entire region, offices and homes together. Nobody got a pass.
Here’s the uncomfortable part for co-managed IT. Your internal IT lead lives in the same metro as your office. On the morning after a storm, that person may be clearing a driveway, fueling a generator or checking on family. That’s not a lack of commitment. It’s geography.
Fully managed doesn’t magically fix it. A Houston provider’s engineers lose power too. The difference is bench depth and remote reach. A provider with people in more than 1 metro can run your cloud tenant, your backups and your help desk from a city that still has electricity. Uprite has offices in Houston, San Antonio and Dallas, which is part of how we plan for that. Our co-managed teams work with companies in Houston, San Antonio and Dallas.
Whichever model you pick, get the storm plan in writing. Who gets dispatched, from where, and within how many hours. Our guide to after-hours and holiday coverage SLAs shows the clause language, and our Houston hurricane disaster recovery guide covers the backup side.
A 6-Question Fit Test for Texas Companies
Answer these honestly. Count your yes answers. Keep score.
- Does someone on your payroll hold the admin credentials today, and could they hand you a current list by tomorrow?
- Could that person produce evidence for every control your SB 2610 tier expects?
- Does that person have the authority to approve changes without escalating to you?
- Would that person know how to declare a security incident and start the 30-day Attorney General clock?
- Is there a backup for that person during vacations, illness or a storm?
- Do you run systems an outside team would struggle to learn, like a custom ERP or a plant floor network?
5 or 6 yes answers point to co-managed IT. Your team owns the environment and needs depth behind it. 2 or fewer point to fully managed IT, even if you employ an IT person today.
3 or 4 is the honest middle. That’s where a scoped co-managed agreement with a written handoff list tends to work well, and it’s also where the arrangement tends to fall apart when nobody bothers to write that list down.
Where Does Each Model Go Wrong?
Co-managed IT breaks at the handoff
The classic failure is an unwritten split. It’s easy to picture. The provider assumes the internal lead is testing restores. The internal lead assumes the provider is. Nobody is.
The second failure is a single point of failure dressed up as a partnership. If your 1 IT person resigns, the provider suddenly holds an environment it was never asked to own. Our page on co-managed IT for a one-person IT department explains how to structure the relationship so a resignation doesn’t turn into a crisis.
Fully managed IT breaks at the edges
Fully managed goes wrong when the business runs something unusual. A custom line-of-business app. Plant floor equipment. A lab instrument tied to an old Windows controller.
A good provider can support those. It’ll learn them slowly, though, and your staff will feel every week of that learning curve, especially if the one person who understood the system has already left by the time the provider arrives. It also goes wrong when an owner signs a fully managed agreement and stops paying attention. The keys table above still has 2 rows with your company’s name on them.
My honest take
Most Texas companies with 20 to 99 employees can make either model work. Price rarely decides it. What decides it is whether the person you’d co-manage with actually wants the job. Ask them.
Some IT leads want to own the environment and would welcome a bench behind them, because they finally get to spend their weeks on projects instead of password resets, vendor calls and after-hours alerts. Others would rather hand it off and focus on the business systems they know best. Neither answer is wrong. And if you’re weighing co-managed IT against another internal hire, the second-hire arithmetic runs those numbers for a 75-person company.
What Texas Owners Ask Before Picking an IT Model
Does SB 2610 require a Texas business to use a managed IT provider?
No. The law rewards a qualifying cybersecurity program with protection from exemplary damages, and it doesn’t specify who runs that program.
A capable internal team can meet it alone. What matters is that the program exists, matches your size tier, and has records behind it on the day a breach happens.
Who signs the cyber insurance application under co-managed IT?
An officer of your company signs it, under either model.
The difference is who checks the answers. Under co-managed IT, your IT lead should verify every control question, such as MFA coverage and backup testing, against what the provider actually runs. Under fully managed IT, the provider supplies those facts, and you should ask for the evidence behind them before anyone signs.
Can our IT manager stay in charge if we choose fully managed IT?
Not really, and it’s better to settle that up front.
Fully managed means the provider holds administrative authority. If you want your IT manager making the calls, that’s co-managed IT by definition, and the contract should say so. A fully managed agreement can still give your manager reporting, visibility and a seat in planning meetings.
How fast does a Texas business have to report a data breach?
Within 30 days to the Texas Attorney General when 250 or more Texas residents are affected, and within 60 days to the affected individuals.
The Attorney General notice is filed through an electronic form on the office’s website. The clock runs from the day you determine a breach occurred, so agree in advance who makes that determination.
Does co-managed IT cost less per user than fully managed IT?
Usually not by much.
Uprite’s fully managed plans run $91 to $138 per user per month, and our co-managed partnership starts at $100. Co-managed savings come from scope, since your internal team keeps part of the work, rather than from a lower rate for the same work. A security-only tier starting at $40 per user is the cheaper route for teams that only need the security layer.
Should a company with offices in Houston and Dallas use a different model in each city?
Rarely, because 2 models means 2 sets of admin rules and 2 incident processes.
The more common pattern is 1 model company-wide, usually co-managed with the IT lead at headquarters, plus provider on-site coverage for whichever office has no IT staff nearby.
Find Out Which Model Your Team Can Actually Own
Send us your current admin credential list, or tell us you don’t have one. That’s a useful answer too. We’ll walk through the keys table with you, map your headcount to its SB 2610 tier, and tell you which model fits. If your internal team should own more than you expected, we’ll say so plainly.
To see what each engagement covers, compare Uprite co-managed IT with fully managed IT services across Texas. Both come with a 120-day satisfaction guarantee.
Not sure which model your team can own?
Speak to an IT ExpertNo cost and no obligation. If your team should own more, we will tell you.