MDR costs more than EDR because you are paying for people. EDR is software that flags an attack on a laptop or server, and MDR adds outside analysts who read those alerts around the clock and act on them.
The question usually comes up when a Dallas owner puts two quotes side by side, one for an endpoint license and one for a managed service, and the second is 5 to 13 times higher. This post explains what that difference pays for, prices it for a 100-person company in Dallas-Fort Worth, and shows when you can skip it. For the service itself, see our page on managed detection and response in Dallas.
EDR finds suspicious activity on your devices, and MDR puts analysts on those alerts 24 hours a day. For 100 users in Dallas, Microsoft’s EDR lists at $3,600 a year, our monitored plan with response starts at $48,000, and staffing 24/7 coverage yourself costs about $669,000 in wages. If nobody on your team can act on an alert overnight, the managed service is the cheaper choice.
What is the difference between MDR and EDR?
EDR (endpoint detection and response) is software on laptops and servers that records what runs on them, flags behavior that looks like an attack, and can cut a device off the network. MDR (managed detection and response) is a service in which a provider’s analysts run that software for you day and night and respond to what it finds.
Most MDR services are built on top of an EDR product. So the real decision is who operates the tool and who is allowed to act on it. Our EDR vs MDR vs XDR guide covers XDR and SIEM as well, and this post sticks to the price gap. For the firms that sell MDR around Dallas, see our ranking of the best MDR providers in Dallas.
What did the City of Dallas attack show about after-hours alerts?
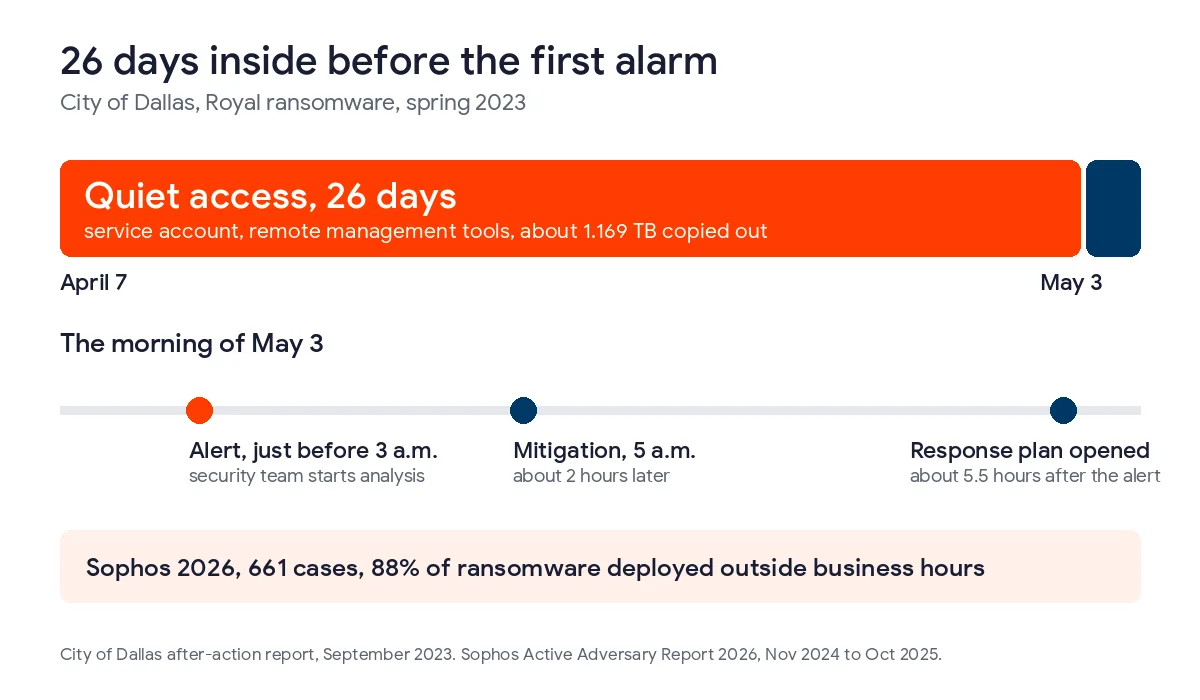
The City of Dallas published a detailed account of its own ransomware attack, and the timeline is useful for any business weighing MDR. According to the city’s after-action report, the Royal ransomware group got into the network around April 7, 2023, through a city service account. Over the next 4 weeks it moved between city systems with legitimate remote management tools and copied out an estimated 1.169 TB of data.
The encryption started on May 3. The city’s security team identified a possible attack shortly before 3 a.m. and began its analysis right away. Mitigation started at 5 a.m., and the formal incident response plan was opened about 5 and a half hours after that first alert. The City Council later approved $8.5 million for recovery, and the city told federal health regulators that information on 30,253 people may have been exposed.
Two details matter for a business owner. The city had people who picked up an alert in the middle of the night, which most 50-person companies do not have. And the attackers spent 26 days inside before anything set off that alert. During those weeks the activity looked like ordinary logins and admin tools, which endpoint software is not good at catching on its own. Looking for that kind of quiet activity by hand is the threat hunting part of a good MDR service. We can’t say whether any provider would have caught Royal sooner, and anyone who claims they could is guessing.
The overnight timing was typical. Sophos reviewed 661 incident response and MDR cases from November 2024 through October 2025 and found that 88% of ransomware was deployed outside business hours.
What does the extra cost of MDR pay for?
Mostly labor, plus permission to act without waking you up. Use this table to check any quote line by line.
| Task | With an EDR license | With MDR |
|---|---|---|
| Record and flag suspicious activity | The software does it | The same software does it |
| Read each alert and decide if it is real | Whoever on your staff sees it | The provider’s analysts |
| Cover nights, weekends, and holidays | Only if you pay someone to be on call | Part of the monthly fee |
| Cut an infected laptop off the network | Possible, if someone is awake to do it | Done by the analyst, if the contract allows it |
| Look for intruders who haven’t triggered an alert | Not included | Included with most of the stronger providers |
| Write up what happened | You read the console yourself | The provider sends a report |
The fourth row is the one to read closely. Some contracts let analysts isolate a device on their own authority. Others require them to call you first, and at 3 a.m. that call can go unanswered for hours.
What would 24/7 coverage cost to build in Dallas?
The Bureau of Labor Statistics counts 7,080 information security analysts in the Dallas-Fort Worth-Arlington metro, with a mean annual wage of $133,790 and a median of $133,610, according to its May 2025 wage estimates. A week has 168 hours and 1 analyst works about 40 of them, so round-the-clock coverage takes at least 5 people once you allow for vacations and sick days. Five analysts at the DFW mean comes to $668,950 a year in wages alone.
A bigger talent pool doesn’t make it cheaper. DFW has more than 3 times as many of these analysts as Houston, and the mean wage here is still $6,910 higher.
| Option for 100 users or devices | Who acts on a 3 a.m. alert | Yearly cost |
|---|---|---|
| Microsoft Defender for Business at $3 per user per month | Nobody, unless you arrange it | $3,600 |
| CrowdStrike Falcon Pro at $99.99 per device per year | Nobody, unless you arrange it | $9,999 |
| Uprite MSSP Security Focus, from $40 per user per month | Our SOC analysts | From $48,000 |
| 5 in-house analysts at the DFW mean wage | Your own staff | $668,950 in wages |
Both license prices are published, by Microsoft for Defender for Business and by CrowdStrike for its Falcon bundles. CrowdStrike does not list a price for its managed tier, so it isn’t in the table. Our row is the starting rate on the pricing page, and licensing is billed on top of it.
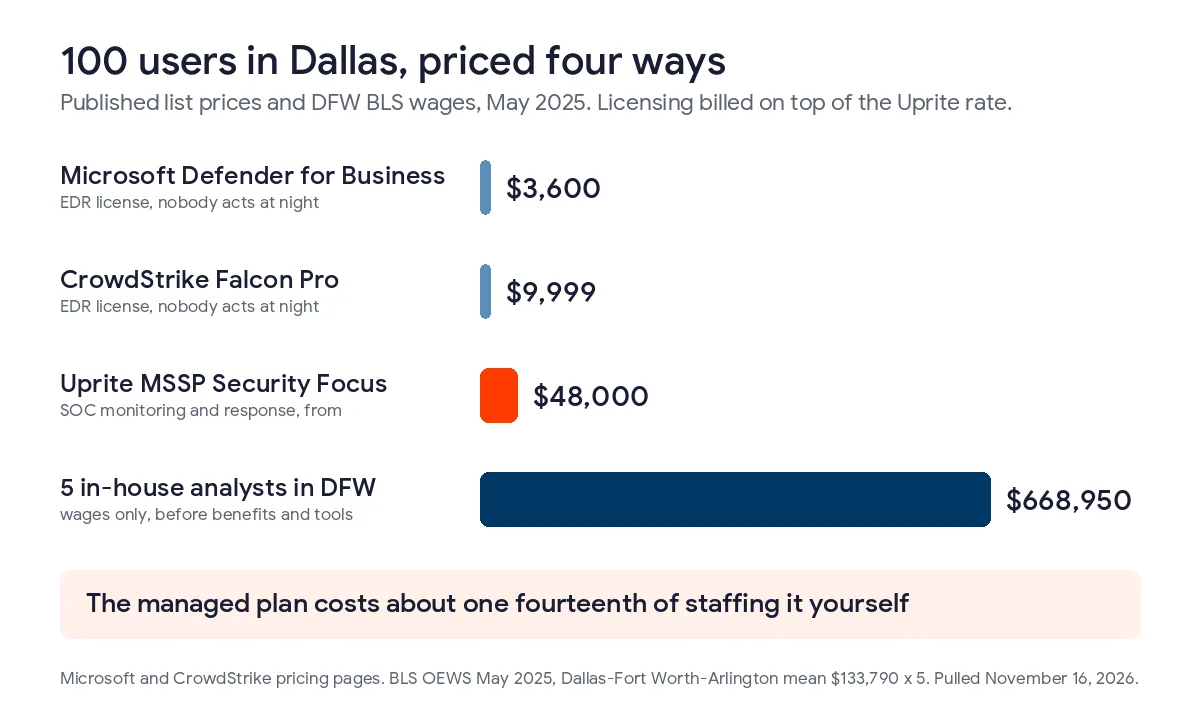
For this company, the managed plan costs about $38,000 a year more than the CrowdStrike license and about $44,400 more than the Microsoft one. It also costs roughly one fourteenth of the in-house team. Owners tend to compare the monthly fee with the license and stop there, when the fairer comparison is with the people they would otherwise have to hire. Our MDR cost guide for Dallas breaks down the monthly fee itself.
When is EDR alone enough for a Dallas business?
It is enough when a named person will act on an alert at any hour. If alerts land in an inbox that nobody checks on Saturday night, it isn’t. Here is how we would decide.
| If this describes you | What we recommend | Why |
|---|---|---|
| Under 15 staff, Microsoft 365 Business Premium already licensed, and one person who checks alerts every evening and weekend | Use the Defender EDR you already pay for | No added cost, and someone is accountable |
| 1 or 2 IT people and no overnight on-call | MDR | An alert at 2 a.m. has nobody to answer it |
| An insurer’s questionnaire or a customer contract asks about 24/7 monitoring | MDR | You need coverage you can show in writing |
| A security team of 4 or more with a night rotation that works | EDR plus an outside SOC for nights and holidays | You keep control during the day |
| An alert-only plan, including our IT Essentials tier | Move to a plan that includes response | Alerts with no response leave the overnight gap open |
The last row is about one of our own plans. IT Essentials runs the Microsoft Defender stack with alerting only and no response, and it is priced for small teams with basic needs. If overnight coverage matters to you, it is the wrong plan, and we will tell you so.
Texas law adds a deadline to all of this. When a breach affects 250 or more Texas residents, the Texas Attorney General must be notified within 30 days of the business determining that it happened, and the office publishes those reports. IBM’s 2026 Cost of a Data Breach report puts the global average breach at $4.99 million. Very large companies pull that average up, so a 100-person firm should read it as a ceiling and not a budget.
What should you ask before signing an MDR contract?
Quotes differ mainly in what they leave out. Put these 6 questions to every provider, us included.
- Are endpoint licenses in the price, or billed as a separate line?
- Can your analysts isolate a device without reaching us first, and does the contract say so?
- How many minutes from alert to action, written as a number?
- How many incident response hours are included before hourly billing starts?
- What do you watch beyond endpoints, such as Microsoft 365 sign-ins, email, and firewall logs?
- How and when do we get our logs and data back if we leave?
Vague answers such as “rapid response” or “licensing varies” usually mean the number isn’t in the contract. Our cybersecurity cost guide for Dallas covers the rest of the security budget, and the 24/7 IT support in Dallas page explains what our team answers after hours. If an insurer is pushing the decision, read our breakdown of cyber insurance requirements in Dallas.
What Dallas owners ask about MDR and EDR
Is MDR worth paying for if we already have EDR?
It is if nobody on your staff can respond to alerts at night or on weekends. The EDR will still find the problem, and MDR gives you a person who acts on it. If you do have someone on call every night, check who actually answered the last 3 after-hours alerts.
How much more does MDR cost than EDR for 100 users?
About $38,000 to $44,400 more per year in our example. That compares CrowdStrike Falcon Pro at $9,999 and Microsoft Defender for Business at $3,600 with our MSSP Security Focus plan starting at $48,000. Licensing is billed on top of our starting rate, and the final price depends on your environment.
Does Microsoft 365 Business Premium include MDR?
No. It includes Defender for Business, which is EDR software with some automated investigation, but nobody is assigned to watch your alerts. You still need staff or a provider to respond.
Why does in-house 24/7 coverage take 5 people?
A week has 168 hours and one analyst works about 40 of them. Four people would cover 160 hours with no time off at all, so a fifth is needed for vacations, sick days, and training. In DFW that team costs about $668,950 a year in wages.
Would MDR have stopped the City of Dallas ransomware attack?
Nobody can say that honestly. The city’s team spotted the attack shortly before 3 a.m. on May 3, 2023, but the attackers had already been inside for 26 days and had copied about 1.169 TB of data. That earlier, quieter stretch is what threat hunting is meant to find.
Does Uprite include EDR licenses in its MDR pricing?
Licensing is billed on top of our starting rates. We quote after reviewing your environment and list exactly what is included, so you can line our proposal up against any other one item by item.
Send us your current endpoint license details and any security quote you have received. We will show you which hours of the week nobody is watching, what closing that gap costs for your headcount, and whether you need to close it at all. We usually reply within 5 minutes.
Talk to a Security ExpertPrefer email or a phone call? Reach the team through our contact page.