A penetration test for a Houston business typically runs about $3,700 to $18,700 in 2026, which works out to 3 to 15 tester-days at $155.78 an hour, the median federal ceiling rate for penetration testers.
That range is a budgeting tool, not a quote, and it isn’t our price list. Uprite performs tests itself and quotes each one by scope, and we also handle the scoping, the cleanup before it, and the fixes after. If you want the bigger picture of what gets tested and how we run it, start with our page on penetration testing in Houston. This guide sticks to money, and to the public data behind every figure in it.
Plan on roughly $1,250 per tester-day at the federal median rate. A narrow external test is about 3 days, external plus internal about 8, and adding a web application and a retest pushes it toward 15. The FTC Safeguards Rule and PCI DSS can require an annual test, small financial firms below 5,000 consumers are exempt from the FTC testing clause, and scanning first is the cheapest way to shrink the bill.
What does a penetration test cost in Houston in 2026?
A penetration test is a paid engagement in which a qualified tester, working under a signed scope, tries to break into your systems the way a real attacker would and then reports what worked. The price comes down to how many tester-days the scope needs, multiplied by the tester’s day rate.
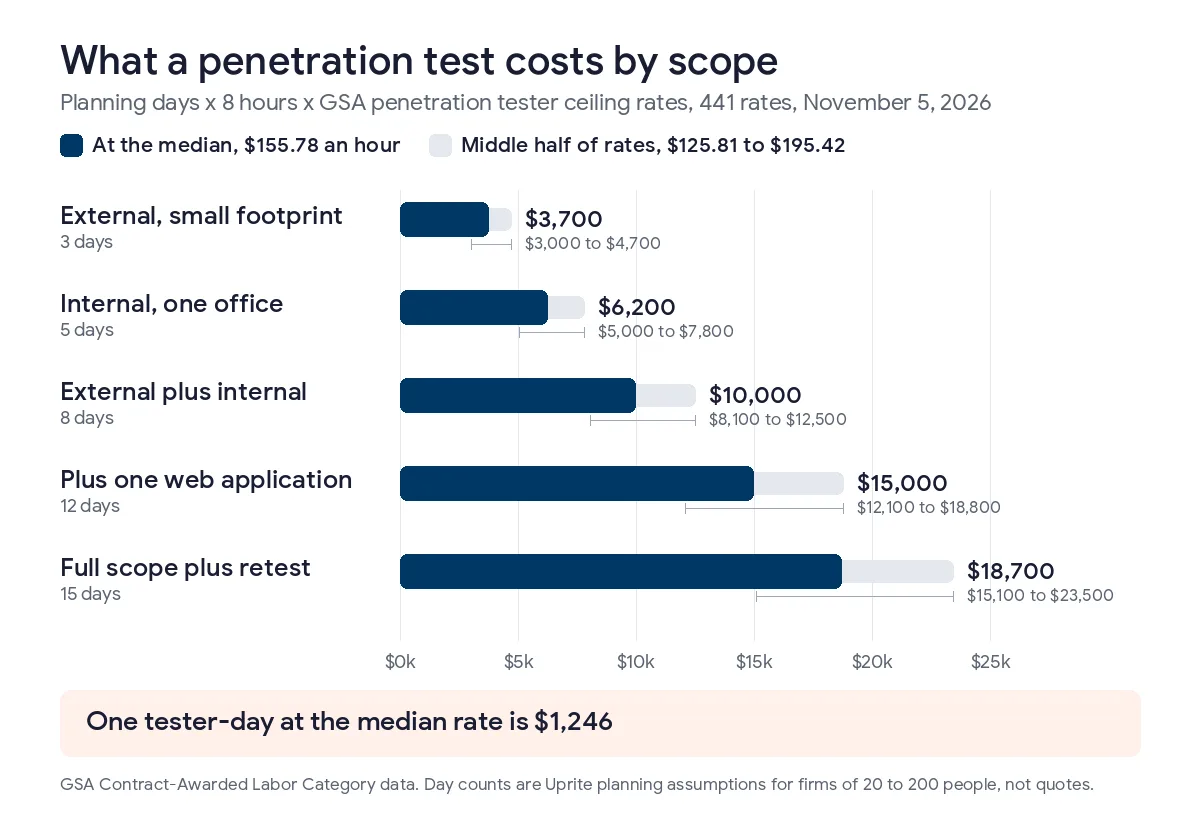
So we priced the days. The rate we use is the median ceiling rate across 441 penetration-tester labor categories on GSA’s federal schedules, pulled on November 5, 2026. At $155.78 an hour, one 8-hour tester-day costs $1,246. The table runs that rate through 5 common scopes, with the middle half of the market shown alongside it.
| Scope | Planning days | At the median rate | Middle half of rates |
|---|---|---|---|
| External network test, small internet footprint | 3 | About $3,700 | $3,000 to $4,700 |
| Internal network test, one office | 5 | About $6,200 | $5,000 to $7,800 |
| External plus internal | 8 | About $10,000 | $8,100 to $12,500 |
| External, internal, and one web application | 12 | About $15,000 | $12,100 to $18,800 |
| Full scope above plus a retest after fixes | 15 | About $18,700 | $15,100 to $23,500 |
The day counts are our planning assumption for firms of 20 to 200 people, and your tester’s written scope sets the real number. Still, they give a finance lead something better than “it depends” to put in next year’s budget.
Where does the $155.78 hourly figure come from?
It comes from GSA’s Contract-Awarded Labor Category data, the public record of hourly rates that vendors have been approved to charge federal agencies. We searched it for penetration tester labor categories and got 441 rates from 142 vendors. The median was $155.78, the middle half sat between $125.81 and $195.42, and the full spread ran from $57.34 to $320.56 an hour.
Experience moves the rate more than anything else in that data. Testers listed with 3 years or less had a median of $133.22. At 4 to 7 years it was $162.30, and at 8 years or more it reached $192.97, which is 45% above the junior figure. Ask who will actually do the work, because a senior name on the proposal doesn’t guarantee senior hours.
One honest caveat. These are ceiling rates, the most a vendor may charge a federal buyer, so they aren’t a commercial price list. Some Houston firms will quote under them and boutique shops will quote over them. We use them anyway because they’re the only large, public, checkable set of tester rates, and you can look up every number in this guide on GSA’s pricing tool yourself.
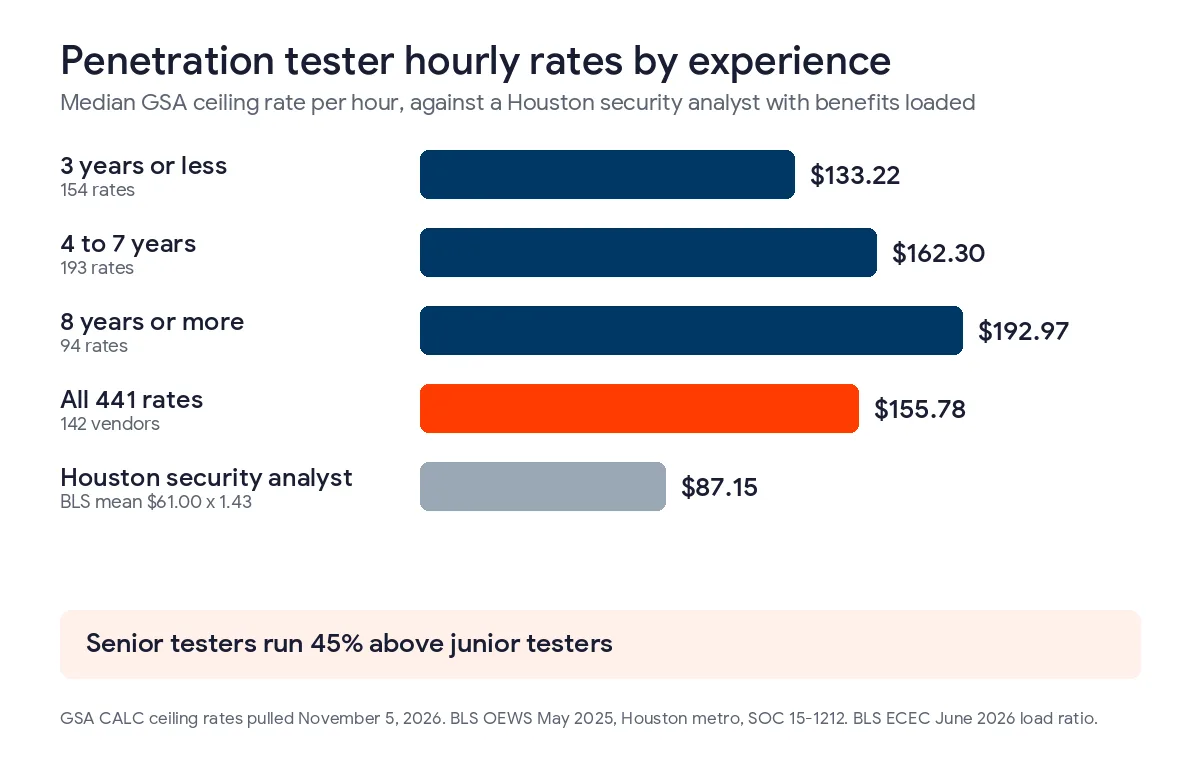
Compare that with a hire. The Bureau of Labor Statistics puts the mean wage for information security analysts in the Houston metro at $61.00 an hour, or $126,880 a year, across 2,110 jobs in its May 2025 wage survey. Add benefits at the 1.43 ratio in the BLS Employer Costs for Employee Compensation release and one analyst costs about $181,300 a year. Most analysts defend networks, too, rather than attack them. That’s why firms our size buy testing by the engagement and keep the yearly budget for people who fix things.
What moves a Houston pen test quote up or down?
Scope does nearly all the work. Before you compare 2 quotes, check that they price the same thing, because a cheap quote often covers half the targets of an expensive one. These 6 factors move the number most.
- How many internet-facing addresses and systems are in scope, since each one adds discovery and testing time.
- Whether the tester starts outside the network, inside it, or both.
- Custom web applications or customer portals, which take far longer to test than a firewall.
- Tester experience, worth roughly a 45% swing in the federal rate data.
- Whether a retest after you fix the findings is included or billed later.
- Fragile systems that need slow, careful testing, like plant-floor controllers or an old line-of-business server.
That last one comes up a lot around Houston. A Pasadena fabrication shop or a Channelview terminal office may have equipment on the same network as the front desk, and nobody wants a test that knocks a controller offline at 2 in the afternoon. Excluding those systems or testing them after hours adds days. Plan for it.
Timing matters as well. We schedule around month-end close, payroll runs, and hurricane watches, because a test squeezed into a bad week gets rushed or cut short. Neither one is cheap.
Do Houston businesses have to buy a penetration test?
Some do. No Texas law orders a private business to run one, but a federal rule, a card brand standard, or a contract can. The table covers the requirements most Houston firms run into.
| Rule or trigger | What it asks for | Who it reaches |
|---|---|---|
| FTC Safeguards Rule, 16 CFR 314.4(d)(2) | An annual penetration test plus vulnerability assessments at least every 6 months, unless you run effective continuous monitoring | Non-bank financial firms such as CPAs, mortgage brokers, auto dealers, and tax preparers |
| Small-firm exception, 16 CFR 314.6 | The testing clause doesn’t apply | Firms holding customer data on fewer than 5,000 consumers |
| PCI DSS v4.0.1, Requirement 11.4 | Internal and external penetration testing at least once every 12 months and after significant changes | Businesses that store, process, or transmit card data |
| HIPAA Security Rule proposal | A test at least every 12 months, proposed in January 2025 and not final as of November 2026 | Covered entities and business associates |
| Cyber insurers and customer contracts | Whatever the application or contract says, often a recent test report | Any firm that signs one |
The FTC wording is worth reading in full, because the continuous monitoring option changes the math. A firm with real 24-hour monitoring and detection can meet the rule without an annual test, according to the text of 16 CFR 314.4. The 5,000-consumer cutoff sits in section 314.6. That’s our reading, not legal advice, so have counsel confirm it for your firm.
The HIPAA change is still a proposal in the Federal Register, and a Houston clinic shouldn’t build a budget around a rule that hasn’t been finalized. Card standards are published through the PCI Security Standards Council, and your acquiring bank decides what proof it wants.
A breach costs more than a test, and Texas adds its own clock. A breach that touches 250 or more Texans has to be reported to the Texas Attorney General within 30 days of discovery, and those reports are posted publicly. A test is one of the few ways to find the open door before somebody else does.
How can you spend less on a pen test without buying a worse one?
Fix the known problems first. A tester billing $1,246 a day who spends a morning confirming a missing patch your own scanner already flagged is the most expensive scan you’ll ever buy. So the order goes inventory, scan, fix, and then test against what’s left.
Each of those earlier steps costs less than a tester-day. Our network assessment is no charge and leaves you with a device inventory and a ranked findings list. Vulnerability scanning is included in our managed security plan from $40 per user per month, and every rate sits on our public pricing page. If your firm falls in a critical infrastructure sector, CISA’s no-cost Cyber Hygiene scanning checks your internet-facing systems too.
Here’s the part vendors rarely say out loud. A “$1,000 pen test” is usually an automated scan with a new label on it. Scans are worth buying, but they answer a different question, and our guide to penetration testing vs vulnerability scanning walks through when each one makes sense. For a version built around Houston firms, see our penetration test vs vulnerability scan guide for Houston. If a quote can’t name the tester, the hours, and the method, you’re probably holding a scan.
Retests are the other quiet cost. A finding isn’t closed until someone proves it’s closed, and a retest bundled into the first quote usually costs less than a separate visit 3 months later. Ask for it up front. When the findings arrive, our guide to how to read a penetration test report ranks them by what to fix first.
How often to pen test in Houston depends on the rule you answer to and how fast your network changes. Once a year is the common floor where a rule names it, and a big change, like a new office network or a cloud migration, is a good reason to test again.
What should a Houston penetration test quote include?
A real quote reads like a work order. If any of these 7 items is missing, ask for it in writing before you sign.
- A target list with addresses, applications, and anything marked off limits
- Testing dates, hours, and an emergency contact on both sides
- The tester’s name and years of experience
- The method, ideally mapped to a public guide such as NIST SP 800-115
- A sample report, so you can see the format before you pay for it
- Whether a retest is included, and for how long after delivery
- A signed authorization letter from someone who owns the systems
We’d add one more check. Ask any provider, us included, how the tester stays independent of the team that runs your IT. Uprite’s own team performs the test, so if we also manage your network, ask how we keep the two apart. A provider grading its own work has an obvious conflict, which is one reason we quote scanning and testing as separate purchases. Our cybersecurity cost guide for Houston prices the rest of the security budget around the test.
What Houston owners ask about pen test pricing
How much does a penetration test cost in Houston?
Plan on about $3,700 to $18,700 in 2026, which is 3 to 15 tester-days at the $155.78 median federal ceiling rate. A narrow external test sits at the low end. External, internal, and web application work with a retest sits at the top. Your tester’s written scope sets the final price.
Why do penetration test quotes vary so much?
Quotes vary because they rarely price the same scope or the same tester. The number of systems, inside versus outside testing, web applications, retests, and tester experience all move the price. In GSA’s rate data, testers with 8 or more years had a median of $192.97 an hour against $133.22 for juniors.
Is a $1,000 penetration test real?
Usually not. At federal median rates, $1,000 buys less than one tester-day, which isn’t enough to scope, test, and write a report. Low prices like that tend to mean an automated scan. Ask for the tester’s name, the hours, and a sample report before you decide.
Does the FTC Safeguards Rule require a penetration test every year?
It requires an annual test unless you run effective continuous monitoring, under 16 CFR 314.4(d)(2). It also requires vulnerability assessments at least every 6 months. Firms with customer data on fewer than 5,000 consumers are exempt from that clause under section 314.6, though counsel should confirm it applies to you.
Can we lower the cost by scanning first?
Yes, and it’s the most reliable way to do it. Scanning and fixing known flaws first means the tester spends paid days on harder problems instead of rediscovering missing patches. Uprite’s network assessment is no charge, and scanning comes inside managed security plans from $40 per user per month.
Does Uprite perform the penetration test?
Yes, Uprite performs the test itself, and each one is quoted by scope. We also write the scope, get your systems ready, and turn the findings into a tracked fix list. If we already run your IT, ask how the testing stays independent of the people managing your network.
How long does a penetration test take to schedule in Houston?
A firm with a current inventory and regular scans can often scope a test within a few days. One with forgotten servers or no admin list needs cleanup first, which can add a month or more. Testing then runs for the planned tester-days, followed by the report and any retest.
Send us the request that’s asking for a test, whether it came from an insurer, a customer, or an auditor. We’ll tell you in writing if a test makes sense now, what to fix first, and what a sensible scope looks like. Our average first response is 5 minutes.
Talk to a Security ExpertPrefer email or a phone call? Reach the team through our contact page, and if you’d rather keep security in-house with outside help on monitoring, see managed security services in Houston.