A San Antonio company with fewer than 20 employees can usually skip a vCISO. The exceptions are clinics, tax preparers, and defense subcontractors. Those 3 need a named security owner at any size. Everyone else starts to need one at around 20 employees.
I run operations at Uprite. We sell security leadership through our vCISO services in San Antonio. We still tell small offices when they don’t need it. A 9-person landscaping company doesn’t need a retainer.
Census counts 43,555 employer locations in the San Antonio metro with fewer than 20 people. Texas asks those businesses for password policies and staff training. A free UTSA program or a few paid hours can cover that. Things change at 20 employees. They also change if you hold patient or tax data, if you sign a CMMC affirmation for a DoD contract, or if a customer asks for your program in writing.
What would a vCISO actually do at a small San Antonio company?
A vCISO is a virtual chief information security officer. It’s a part-time security executive you hire by the hour or by the month. The vCISO decides which risks the owners accept. They write the security program. They answer customer security questionnaires and sign off on the answers.
Say you run a 40-person home health agency on the Northwest Side. Your IT provider patches the laptops and runs the backups. But nobody has decided whether the scheduling vendor should still have patient addresses from 2019. Nobody has written down what happens on the first morning of a ransomware attack. A vCISO handles those 2 things. The patching stays with IT. You don’t want to pay vCISO rates for password resets.
How many San Antonio businesses are small enough to skip one?
The Census Bureau’s County Business Patterns counts employer locations by size. The 2023 data shows 52,088 locations in the 8-county San Antonio-New Braunfels metro. Most are in Bexar County. The other 7 counties are Comal, Guadalupe, Wilson, Medina, Atascosa, Bandera, and Kendall. The table puts each size group next to its tier in Texas law.
| Employees at the location | San Antonio metro locations | Share | What Texas chapter 542 expects |
|---|---|---|---|
| Fewer than 20 | 43,555 | 83.6% | Simplified measures, like password policies and staff cybersecurity training |
| 20 to 99 | 7,011 | 13.5% | Moderate measures, including CIS Controls Implementation Group 1 |
| 100 to 249 | 1,032 | 2.0% | A program that conforms to a recognized framework |
| 250 or more | 490 | 0.9% | Outside the chapter 542 safe harbor |
The tiers come from SB 2610. It took effect on September 1, 2025. It covers businesses with fewer than 250 employees. If you had a qualifying program in place when you were breached, a court can’t award exemplary damages against you. For 20 to 99 employees, the program has to include Implementation Group 1. That’s 56 safeguards. Someone has to put them in place and keep dated records.
Census counts locations, not companies. A 6-person branch of a Dallas firm shows up in the first row. So does a 6-person dental office, and that office still has to follow HIPAA.
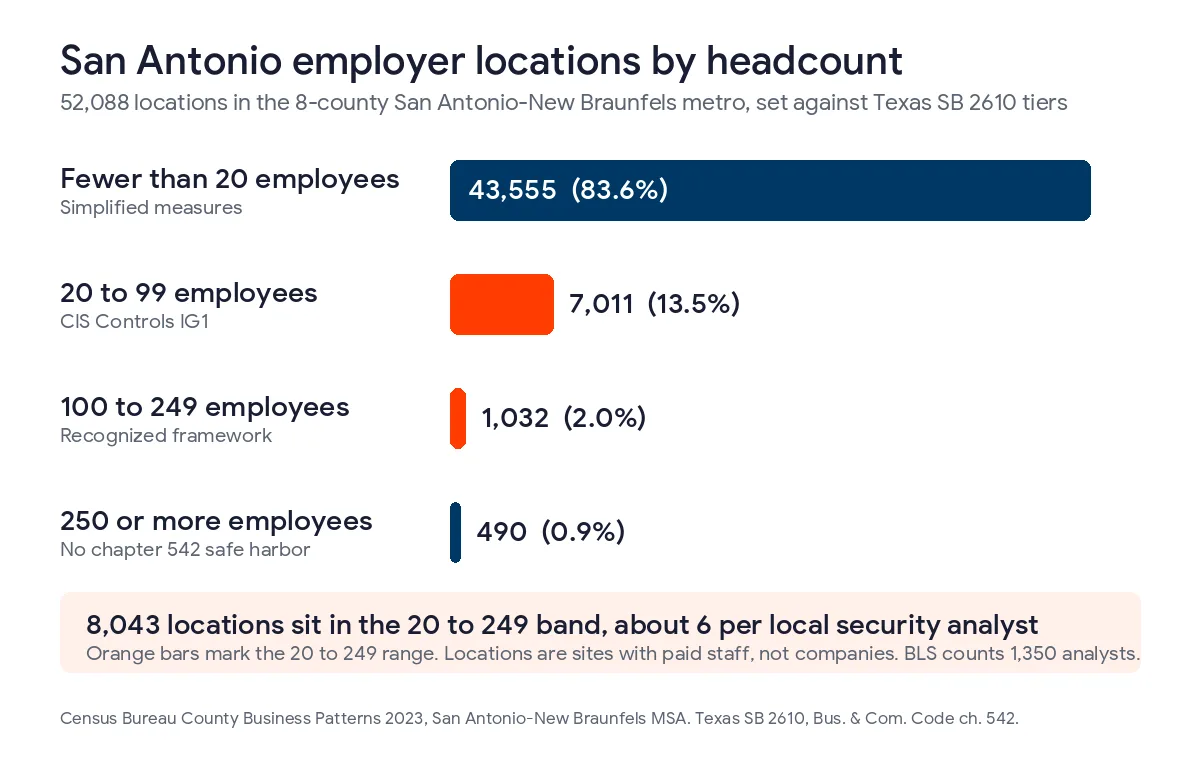
You could also hire your own security person. BLS counted 1,350 information security analysts in the San Antonio metro in May 2025. Their mean pay was $125,830 a year. There are 8,043 locations in the 20 to 249 range. That works out to about 6 businesses for each analyst. Banks, hospital systems, and federal contractors hire from the same group. A 45-person firm would pay $125,830 in salary before benefits, for 1 person.
Which small San Antonio businesses need one anyway?
Headcount isn’t the only test. Three kinds of local businesses fall under rules that require a named person in charge of security. Those rules apply no matter how many people you employ.
Clinics, dental offices, and home health
HIPAA’s 45 CFR 164.308 requires every covered provider to identify a security official. There’s no exception for small practices. Census lists 972 dental offices in the metro. Of those, 927 have fewer than 20 people. There are also 1,981 physicians’ offices, and 1,741 of them have fewer than 20. In a 7-chair dental practice, the security official is usually the office manager. We ask who reviews that person’s work. Often nobody does. Our guide to HIPAA cybersecurity requirements in San Antonio covers the rest of the rule.
Tax preparers and CPA offices
The FTC Safeguards Rule treats tax preparers as financial institutions. There’s a small-firm exemption in 16 CFR 314.6 for firms with data on fewer than 5,000 consumers. It removes 4 duties. You can skip the written risk assessment, the testing requirement, the written incident response plan, and the annual report to leadership. You still need a Qualified Individual to run the program. The metro has 884 accounting and tax locations, and 834 have fewer than 20 people. A 6-person shop with 3,000 clients can name a partner and bring in help as needed. A shop with 7,500 clients doesn’t get the exemption. It needs all of those documents in writing.
Subcontractors on defense work
Joint Base San Antonio brings a lot of small local firms into federal contracting. Since November 10, 2025, new DoD contracts can include the CMMC clause, DFARS 252.204-7021. Under 32 CFR 170.22, a senior person at each contractor affirms compliance in SPRS. They do it after the assessment and again every year. That affirmation goes to the federal government with their name on it. If it’s wrong, the company can face False Claims Act exposure. We don’t recommend signing it based on a verbal OK from your IT provider. Our CMMC scoping guide for San Antonio explains which systems count.
What do San Antonio’s own breach notices show?
The Texas Attorney General posts breaches that affect 250 or more Texans. We pulled its public breach list on November 6, 2026. It had 26 notices from organizations based in the San Antonio area, posted since April 2025. Nine were from health care providers. Three were from law offices. Two were from school districts. The median notice covered 3,197 Texans. Only 4 covered fewer than 1,000.
Four of the dental notices list the same breach start date, May 25, 2026. The offices are in San Antonio, Converse, and Floresville. When several notices share a start date, a shared vendor is often the cause. Someone has to decide which vendors get patient data. Someone has to decide what those vendors owe you when they fail. That’s a vCISO’s job. It isn’t a help desk’s job.
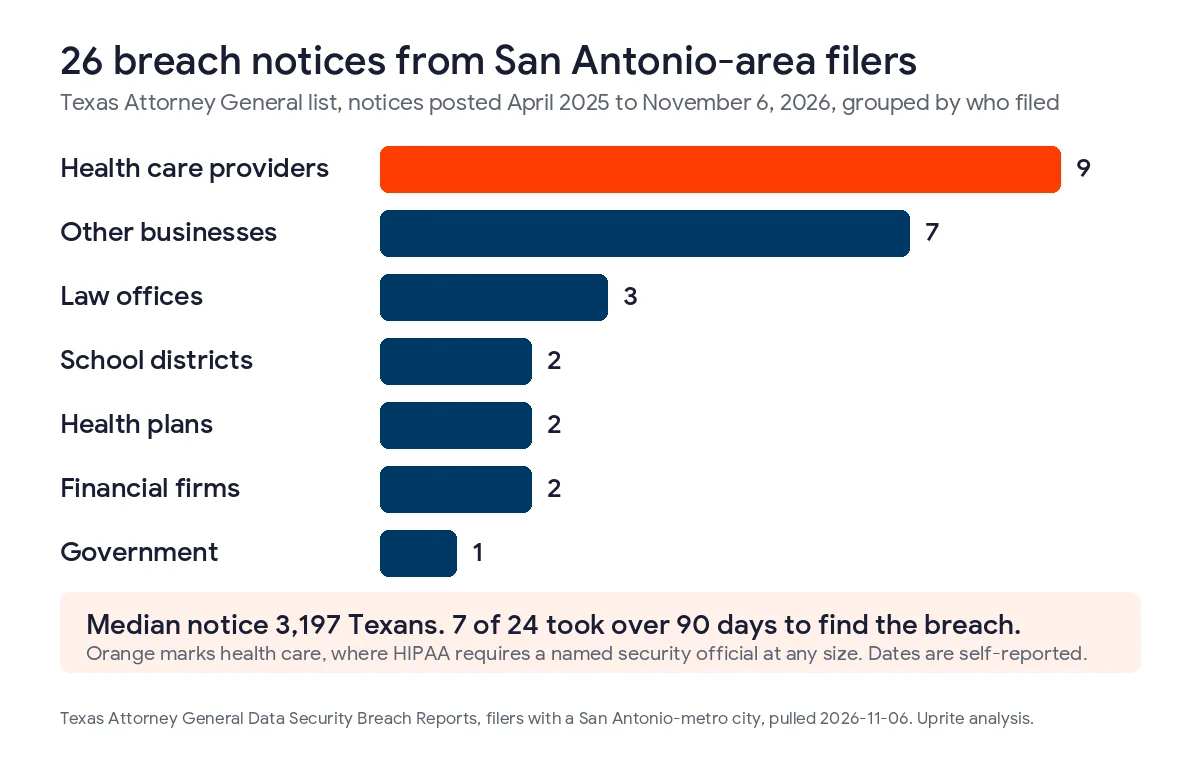
Timing matters too. Of the 24 notices with both dates filled in, 7 took more than 90 days to find the breach. The filers report those dates themselves. Once you determine a breach happened, section 521.053 of the Business and Commerce Code gives you 30 days to notify the AG. That applies when 250 or more Texans are involved. You should name the person who will make that count before you need it.
When can a San Antonio company skip the vCISO?
We tell owners to skip it when all 4 of these are true.
- Your company has fewer than 20 employees.
- You don’t keep patient records, tax files, or defense contract data.
- No customer, lender, or insurer has asked for your security program in writing.
- Your IT provider can show dated records of multi-factor login, tested backups, and patching.
There’s free help in town. UTSA’s Small Business Development Center leads the Texas Small Business Cybersecurity Assistance Center. It offers Texas small businesses up to 40 hours of vCISO help at no cost. A 2-year, $1 million SBA grant pays for it. The grant started in late 2024, so call first and confirm it’s still taking new companies. NIST also publishes a Small Business Quick-Start Guide. An office manager can work through it in a few sittings.
What should you buy, based on where you are?
Find the row that matches your company. If 2 rows match, use the lower one.
| If this sounds like you | Buy this | How often |
|---|---|---|
| Under 20 people, no regulated data, nobody asking | Your IT provider plus the free UTSA and NIST help | No retainer |
| Under 20 people with patient or tax data | A risk assessment and a written program, with a named internal owner | Once, then a yearly review |
| A questionnaire or insurance renewal you can’t answer | A small block of advisory hours | As the questions come in |
| 20 to 249 people, or a CMMC affirmation coming due | A monthly vCISO retainer | Monthly, with a quarterly report to owners |
| A breach, regulator letter, or audit already in motion | A vCISO engagement that starts this week | Right away |
This table is our own rule of thumb. It isn’t a regulation, and it won’t fit every company. A 15-person firm about to sign its first enterprise contract should use a lower row than its size suggests. Our guide to vCISO cost in San Antonio shows what those hours cost here. To compare the firms that sell the work, see our ranking of the best vCISO providers in San Antonio.
Where should you go from here?
If you’re in the bottom 2 rows, our managed security services in San Antonio run the tools a vCISO will ask about. Tax and CPA offices should read our post on client portal security for San Antonio CPA firms before filing season. If you can’t tell whether you need security leadership or IT planning first, read our vCISO vs vCIO comparison for San Antonio. Everyone else can come back to this page when they hire employee number 20.
What San Antonio owners ask us about vCISOs
Is a vCISO the same as my IT company?
No. Your IT company runs your systems. A vCISO decides how much risk the business takes on and writes it down. Some providers do both. If yours does, they can show you a signed and dated security program.
We’re a 9-person dental office. Do we really need one?
You need a named HIPAA security official, and that’s a different thing. Many small practices name the office manager. They buy a yearly risk analysis from an outside firm. A monthly retainer makes more sense when you open a second location or share systems with a larger group.
Does CMMC mean a 15-person subcontractor needs a vCISO?
It means someone senior has to sign a compliance affirmation every year. That signature has legal weight. If nobody on your staff can check the evidence behind it, outside help costs less than a wrong answer. First confirm which CMMC level your contracts require. Level 1 asks for much less than Level 2.
Can the free UTSA program replace a vCISO?
It can for a first pass. Up to 40 free hours can get a small company a starter program. The hours run out, so decide who will own the program after that.
What should a vCISO deliver in the first 90 days?
You should get a risk assessment, a list of fixes ranked by cost, and a written program your owners sign. You should also get a plan that says who calls whom in the first hour of a breach. A long template with your logo on the cover doesn’t count.
At what size does a full-time CISO make more sense?
Usually well past 250 employees, or when audits and contract reviews come every month. BLS puts the mean pay for computer and information systems managers in San Antonio at $166,630. A CISO is a more senior hire than that. Below 250 employees, a part-time executive usually costs less.
Pick the row in the table above that fits your company and tell us which one it is. We’ll tell you whether a vCISO makes sense for your San Antonio business. If it doesn’t, we’ll point you to the free help.
Speak to a vCISO